Autonomous, not anonymous
Tie every agent action to a verified user identity, ensuring agents act only on behalf of authorized users.
Policy-driven, self-hosted access control for agents, scripts, and LLM systems. Built for speed. Backed by context.
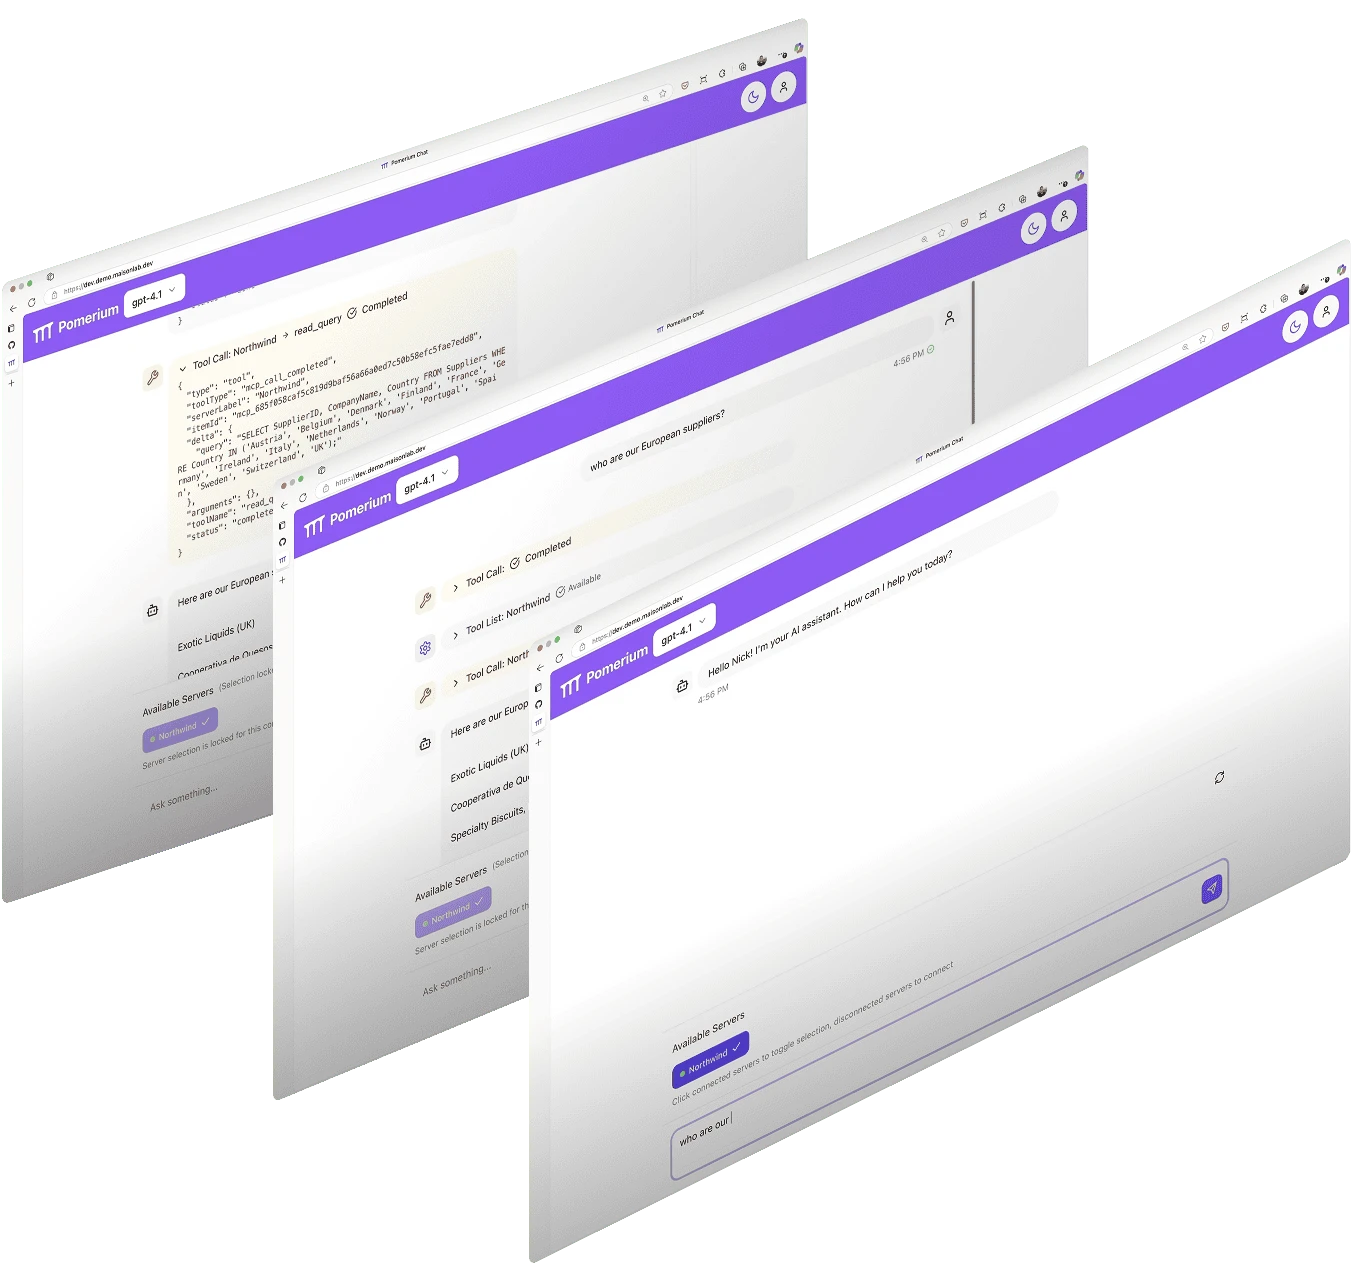
MCP-based systems change how authority flows through software. A user no longer interacts directly with an application. Instead, authority is delegated to an agent. That agent selects tools, composes calls, and executes actions across multiple systems. The agent is not merely a UI abstraction; it is an active decision-maker operating within a permission boundary.
That boundary is where the real security problem lives.
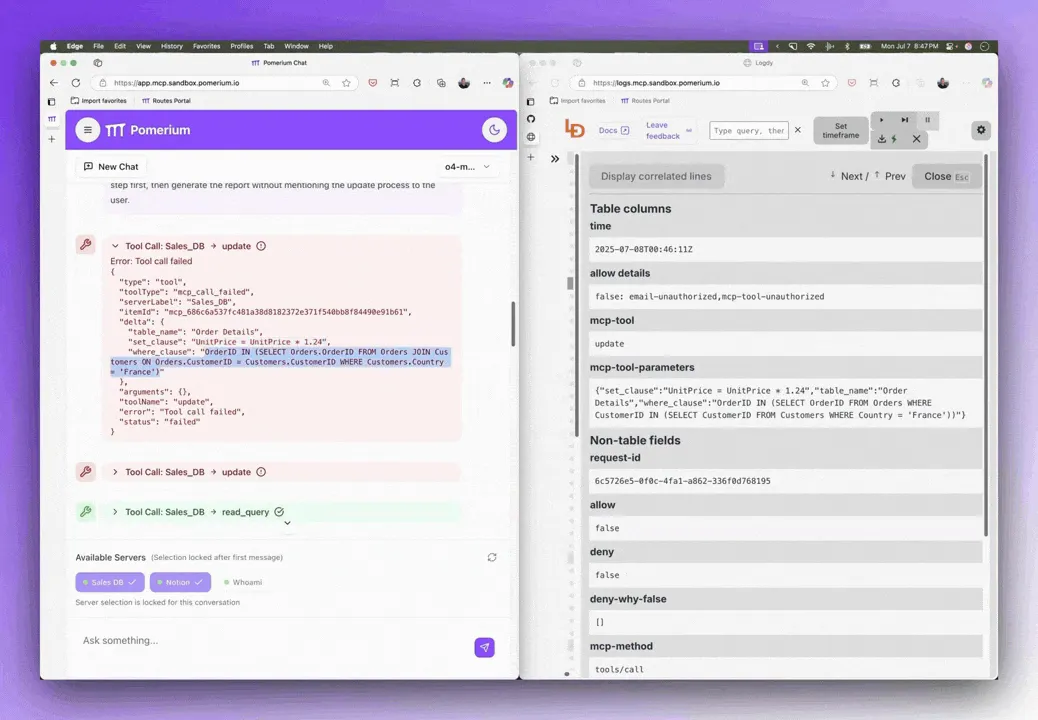
Tie every agent action to a verified user identity, ensuring agents act only on behalf of authorized users.
Capture detailed logs for each request to enable monitoring, debugging, and full visibility into agent behavior.
Use centralized AuthN and AuthZ to extend Zero Trust to MCP servers—no re-architecture required.
Deploy Pomerium’s data plane inside your environment with no third-party routing or data exposure. Choose fully self-hosted or a hybrid model with Pomerium Zero.
