 Quarterly reports
Pomerium Zero
Pomerium hosts the control plane. Pomerium Core runs in your environment.
Typically best for: Teams that want simpler management without running a control plane.
Pomerium is an identity-aware proxy for private applications, services, and AI tools. It verifies identity, checks your access policy, and forwards approved requests.
403 Forbidden
If you should have access, contact your administrator with your request id…
200 OK
user@example.com203.0.113.42status: activeAll this happens in tens of milliseconds.
Identity and context match the policy. The request reaches Grafana.
Identity and context match the policy. The request reaches Grafana.
Select a check to see its policy rule.
Domain is example.com. This request matches the condition.
allow:
  and:
    - domain: example.com
Device approval is true. This request matches the condition.
allow:
  and:
    - device:
approved: trueBetween 09:00 and 17:00 UTC. This request matches the condition.
allow:
  and:
    - time_of_day:
        timezone: UTC
        after: '09:00'
before: '17:00'Within 203.0.113.0/24. This request matches the condition.
allow:
  and:
- source_ip: 203.0.113.0/24United States. This request matches the condition.
allow:
  and:
    - record:
        type: geoip
        field: country
        is: US
Employment is active. This request matches the condition.
allow:
  and:
    - record:
        type: hr_user
        field: status
is: activeAllow ACME, Corp employees with an example.com identity and an approved device when their employment is active and the time, network, and location meet the policy.
Device approval requires Enterprise. HR and location values use Enterprise external data sources.
Domain is example.com. This request matches the condition.
allow: and: - domain: example.com - device: approved: true - time_of_day: timezone: UTC after: '09:00' before: '17:00' - source_ip: 203.0.113.0/24 - record: type: geoip field: country is: US - record: type: hr_user field: status is: activeVerify the identity behind a request with your existing identity provider.
Evaluate the route's access policy using identity and request context.
Forward approved requests to the application. Reject requests that do not meet the policy.
Apply policy at each protected route, with identity, context, and logs in one request path.
Pomerium operates at Layer 7, which makes it protocol-aware. Your users get to use the tools they already know and love, without a janky wrapper command. You get security controls on each request or action.
Use your browser for private web applications and your standard SSH client for native SSH. TCP and UDP tunnels use a Pomerium client.
See protocol-aware policies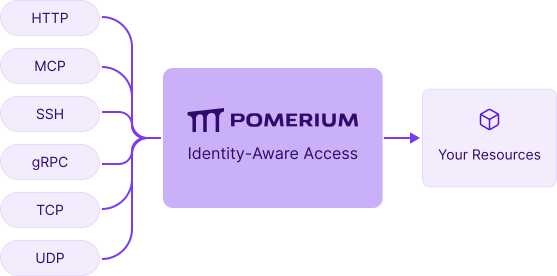
Pomerium checks policy on each HTTP request. Access decisions use the identity and context available when the request arrives.
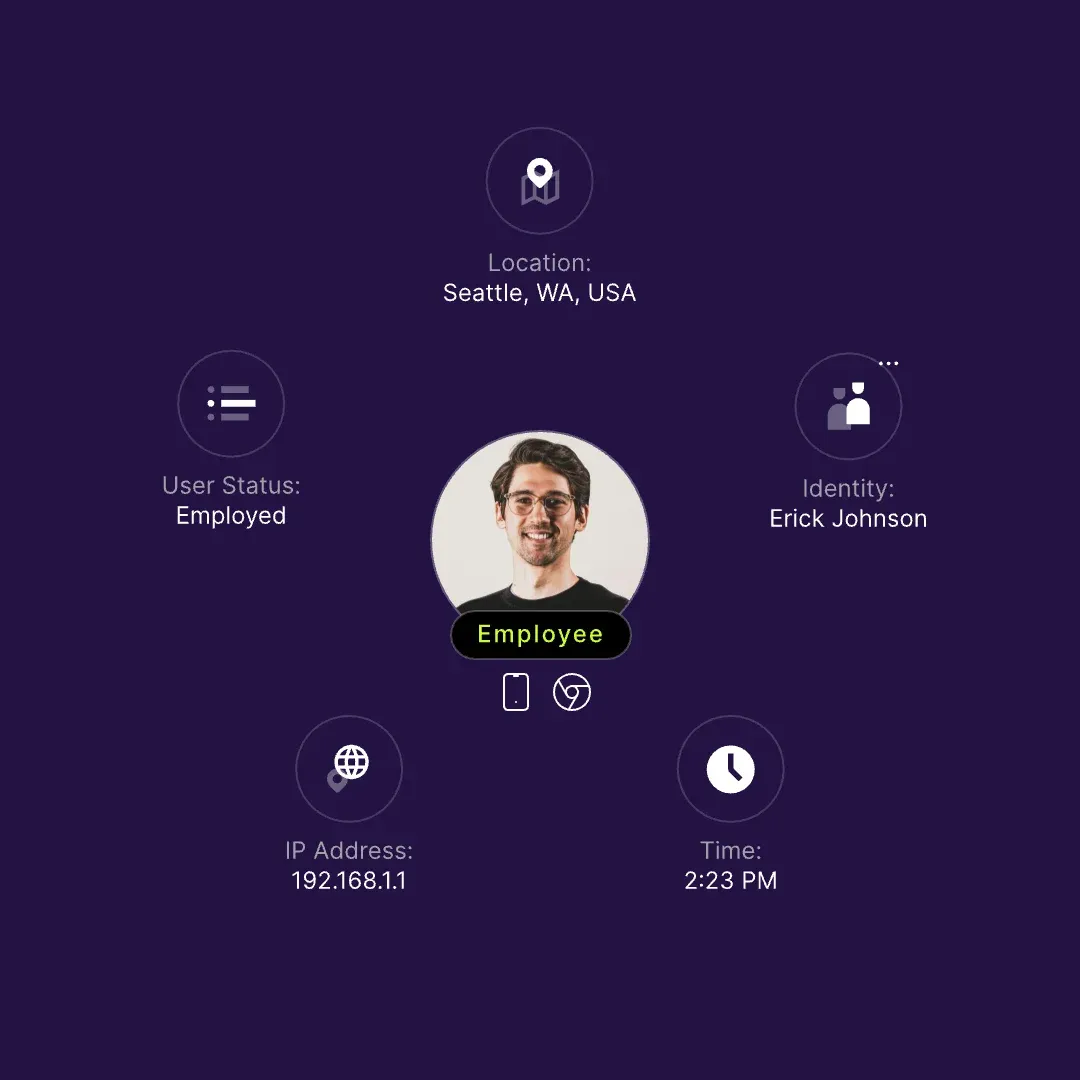
Use identity claims, device information, and external data in your access policies. Connect your identity provider and the systems you already use.
See who requested access, which route they requested, and why the policy allowed or denied it. Send access and authorization logs to your logging system.
Give each identity access to the resources it needs. Pomerium enforces the access policy at the protected route, before forwarding traffic.
Use the same access layer for employees, service accounts, and AI agents, with policies specific to each resource.
Why identity-aware access mattersDefine who can use each route and use authorization logs to inspect the decision.
Add authentication and authorization in front of applications without building a separate login and policy system into each one.
Control access to Kubernetes APIs and applications with identity-based policies.
Give employees and contractors browser access to the web applications they need.
Authenticate access to MCP servers and apply policy to the tools an AI agent can call.
Both editions are built on open-source Pomerium.
Pomerium hosts the control plane. Pomerium Core runs in your environment.
Typically best for: Teams that want simpler management without running a control plane.
You host the control plane and Pomerium Core in your environment.
Typically best for: Large organizations and teams with self-hosting requirements.