How Pomerium Makes Access Audit Ready and Turns It Into a Source of Truth

Sterling Davis
Head of Product Marketing
Head of Product Marketing
Ask most teams to show who accessed a sensitive system—and why—and you’ll get a long pause.
Logs are scattered. Context is missing. And in hybrid environments, the truth is buried under brittle workflows and fragmented policy enforcement.
You can’t secure what you can’t explain.
And when credentials are stolen, explainability becomes your last line of defense.
Audit readiness isn’t just a checkbox. It’s a core capability.
It means:
That level of clarity only comes when access decisions happen at the application layer, with identity and context built in.
Today’s attackers aren’t breaking in—they’re logging in.
Phishing kits, infostealers, and credential marketplaces make unauthorized access look legitimate.
If you’re only logging session starts or network connections, you’re missing the real picture.
Today’s audits demand clear attribution.
Incident response depends on full traceability.
And compliance frameworks now expect real-time visibility and proof.
If you can’t explain access in seconds, you’re not audit-ready. You’re exposed.
Pomerium customers span industries, infrastructure, and workflows but share a common goal: prove every access decision.
This isn’t a wishlist. It’s what customers do with Pomerium every day.
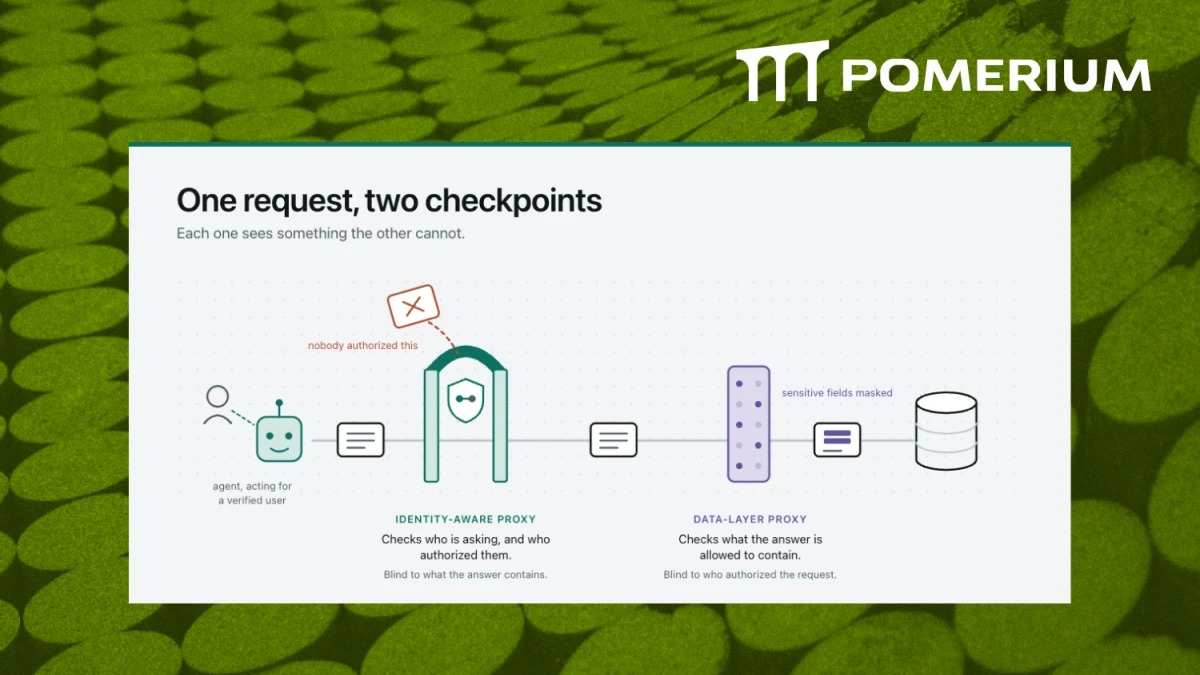
Pomerium is an application-layer access gateway that enforces and logs every request before it reaches your systems.
Because enforcement happens inline, you get complete traceability without stitching together logs or relying on after-the-fact analysis.
Pomerium helps teams align with leading compliance frameworks — and be ready at all times:
Modern security isn’t just about blocking threats. It’s about proving trust.
-> Talk to our team about mapping access control with Pomerium to your compliance and audit goals