tags
Access Control
Browse Pomerium articles tagged Access Control.
Topic archive
Resources Tagged: Access Control
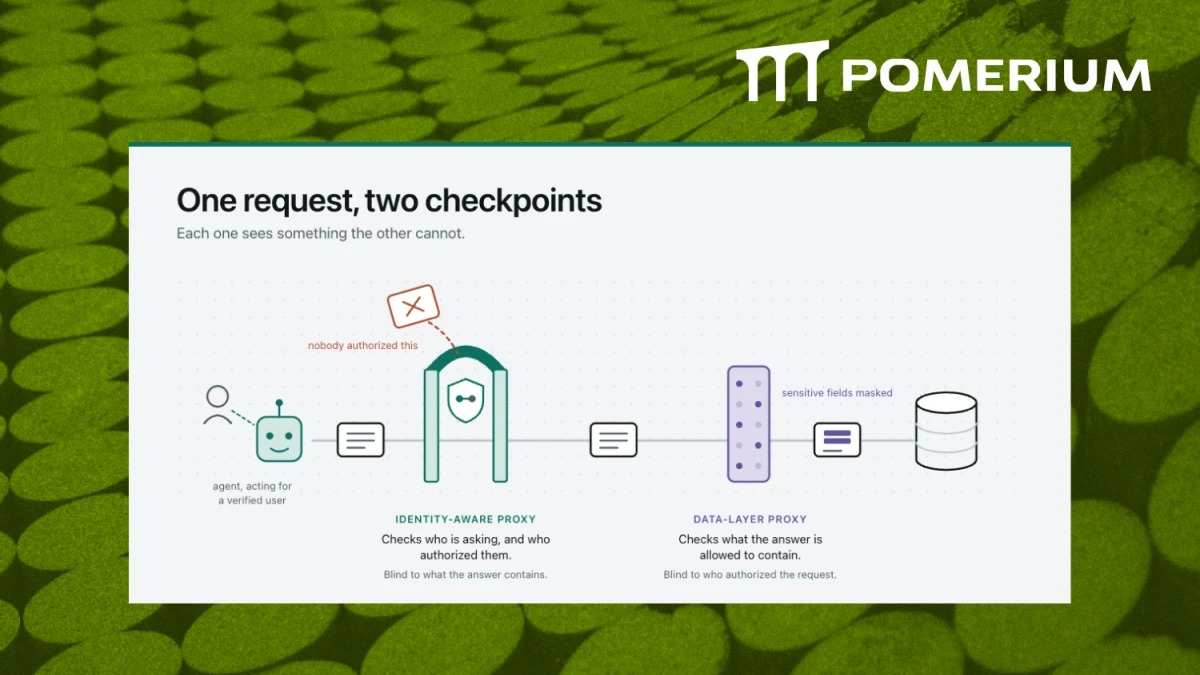
Data-Layer Proxy vs Context-Aware Proxy: Which Do You Need?
Two proxy architectures secure AI agent access, and they solve different problems. How data-layer and context-aware proxies differ, and when you need each.
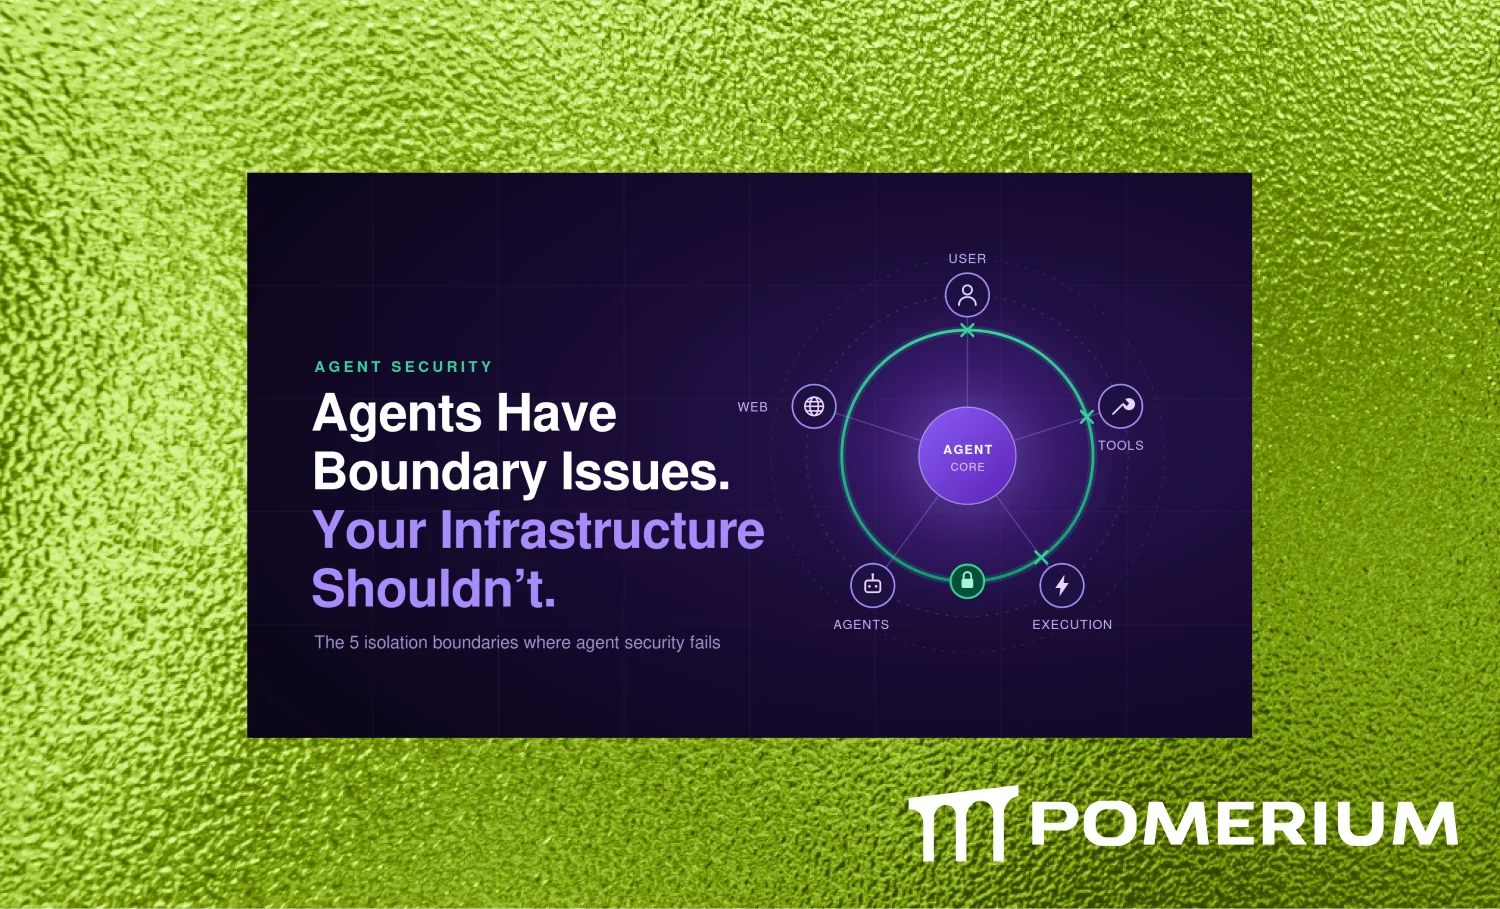
Agents Have Boundary Issues. Your Infrastructure Shouldn't.
Why the five isolation boundaries in agent security research all point to the same conclusion: enforcement has to live outside the model.
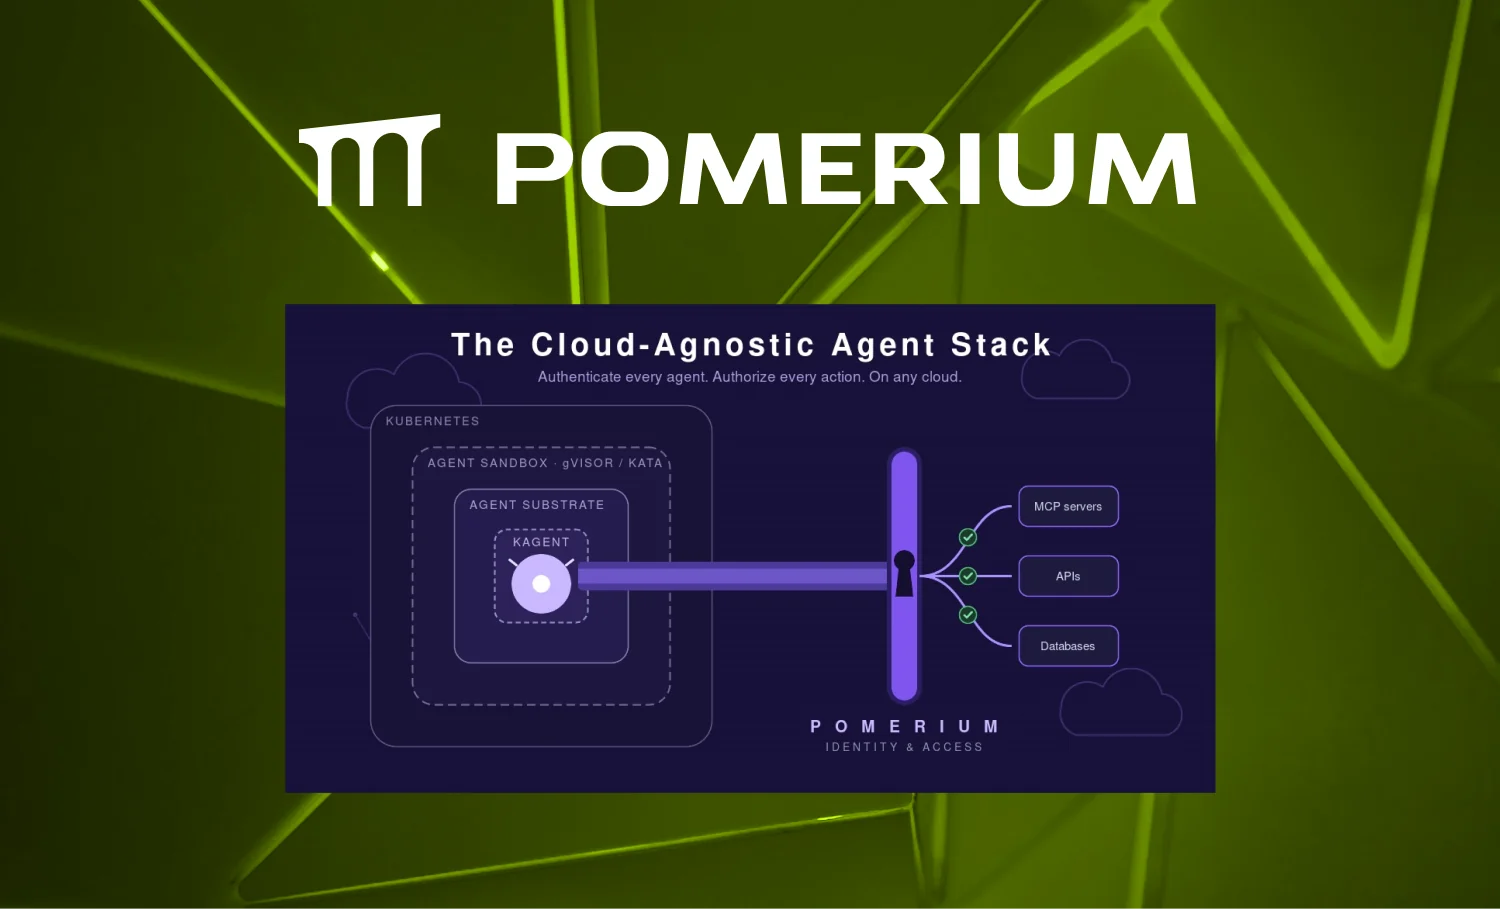
Google Built an Agent Runtime on Kubernetes. Here's How to Build a Cloud-Agnostic One with Identity Included
Google spent the last year quietly admitting what we already knew: Kubernetes was never designed to run AI agents. As Janakiram MSV writes in The New Stack , Google's GKE Agent Sandbox and the new Agent Substrate project amount to an indirect admission "that the platform that won the container decade is not the right control plane for AI agents."
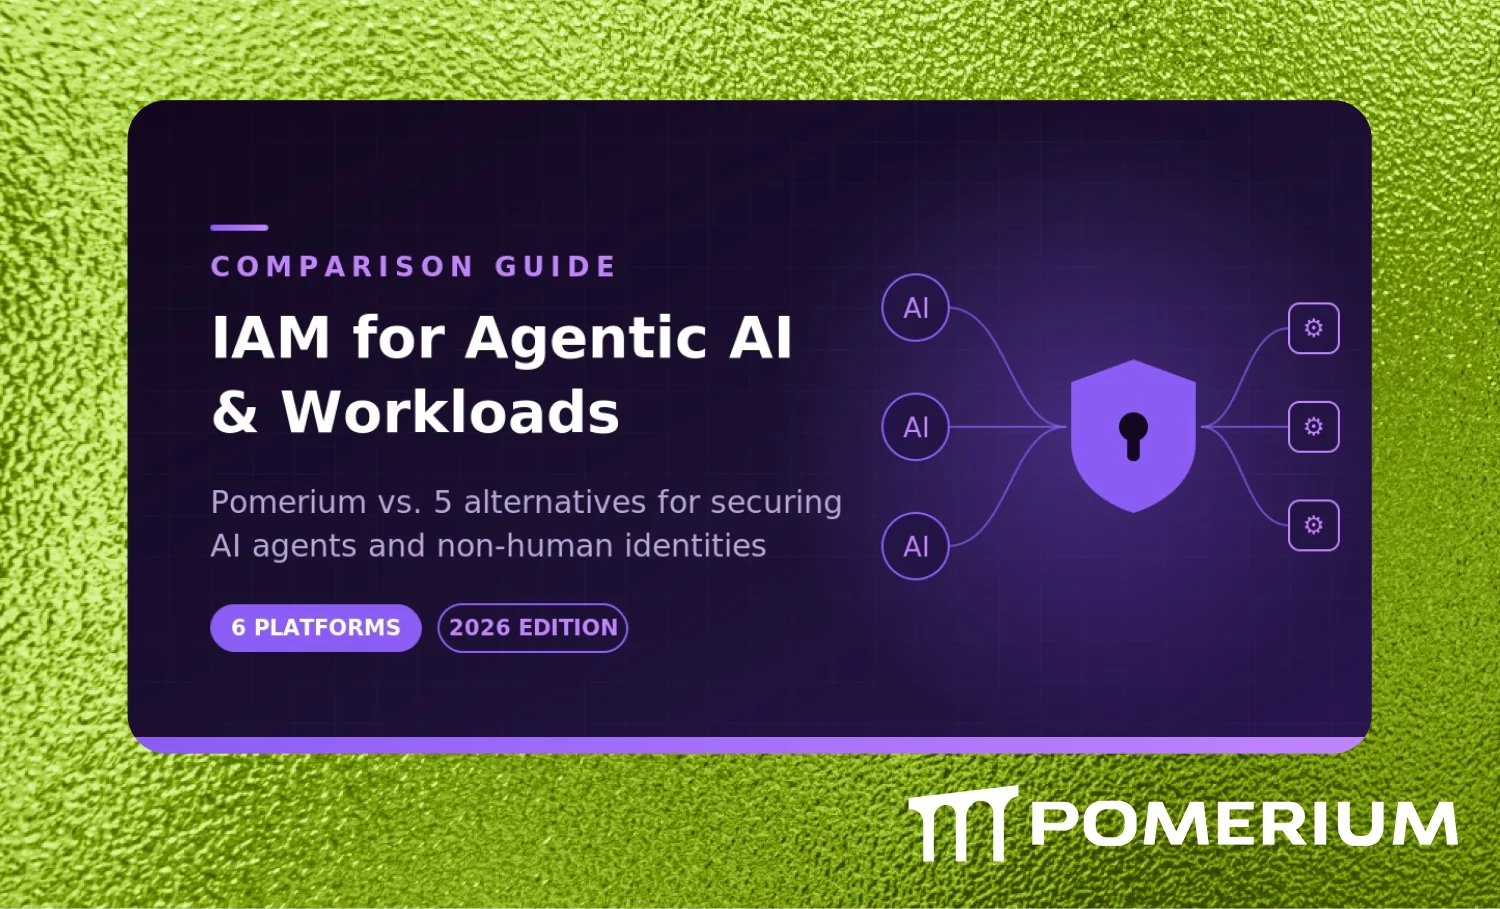
IAM for Agentic AI: 6 Platforms Compared | Pomerium
Compare Pomerium, Aembit, Astrix, Token Security, Oasis, and Britive for securing AI agents and workload identities. See which platform fits your stack.
The AIUC-1 Compliance Checklist: 5 Layers Every Enterprise Needs Before Deploying AI Agents
A quick-reference checklist for AIUC-1 compliance. Five layers, 28 controls, one page. Print it, pin it, pass the audit.
What Is an Agentic Gateway? Definition, Architecture, and Why It's Different from an API Gateway
Discover what agentic gateways are, how they secure autonomous AI agents with tool-level authorization and session-aware policy enforcement, and why API gateways fall short.
Midmarket Security Teams Deserve Better Than Enterprise Hand-Me-Downs
New research shows 42% of midmarket security teams are stretched thin while enterprise tools don't fit. Here's why a zero trust reverse proxy, like Pomerium, changes the equation.
Secure Internal Access to Grafana, Argo, GitLab, and Prometheus Without a VPN
Securing internal tools without a VPN is no longer a fringe idea—it’s becoming the default for modern Kubernetes platforms.
From NGINX to Pomerium: A Practical Migration Guide for Internal Kubernetes Applications
Migrating from NGINX Ingress to Pomerium does not require a disruptive rewrite. Most teams adopt Pomerium incrementally, starting with internal services where the security and operational gains are immediate. An initial objective can be to decouple routing from access control for internal services.
Privilege Access Is the Past. Per Request Authorization Is the Future.
For twenty years, cybersecurity has organized itself around a single idea:
AI Is Your Biggest Security Risk
IBM’s Cost of a Data Breach Report 2025 delivers a surprising headline: for the first time in five years, the global average cost of a data breach has declined, dropping to $4.44M . The reason? Faster detection and containment, driven largely by security automation and AI.
Replacing Ingress-NGINX: A Modern Approach to Secure Kubernetes Access
For years, NGINX Ingress has been the default answer to a simple question: How do I get traffic into my Kubernetes cluster? It excels at Layer-7 routing, TLS termination, and traffic shaping, and for many workloads it remains a solid choice. But as Kubernetes has moved beyond hosting public-facing services and into powering internal platforms , the limitations of traditional ingress have become increasingly apparent.
The OWASP Top 10 for LLMs and How to Defend Against Them
TL;DR — The OWASP Top 10 for Large Language Model (LLM) applications highlights prompt injection, insecure output handling, and data exposure as critical risks. This guide walks through the Top 10 and shows where Zero Trust access controls, starting free with Pomerium Zero , are most effective: LLM01 Prompt Injection and LLM02 Sensitive Information Disclosure.
Why Traditional Access Controls Fail in LLM Deployments
TL;DR: Prompt-driven apps quickly outgrow static API keys and coarse Identity Access Management (IAM) roles. OWASP’s LLM risk list shows why that model breaks. The answer is continuous, identity-aware policy applied before prompts ever reach the model. Pomerium provides that control so teams can ship GenAI features with confidence.
Why the Managed Context Protocol (MCP) Spec Still Leaves Gaping Security Holes
TL;DR — MCP gives AI agents a shared way to invoke tools and complete tasks. But the spec lacks core security features. There is no built-in authorization, no identity enforcement, and no way to apply context-aware policy. Teams relying on reference servers are exposing internal APIs without guardrails. Pomerium applies Zero Trust controls to every request, adding identity, context, and policy enforcement at Layer 7.
How Shadow AI Impacts SOC 2 and HIPAA, and What to Do About It
Shadow AI bypasses critical access and audit controls required by SOC 2 and HIPAA. Learn how per-route policy with Pomerium restores visibility, enforcement, and audit readiness.
Your Employees Are Already Dumping Company Data to LLMs (Here’s What To Do About It)
It's happening right now, in your organization. That senior developer just pasted your global auth tokens into ChatGPT to debug a tricky race condition. Your data analyst uploaded last quarter's customer churn data to Claude to help write their board presentation. Your product manager is feeding competitive analysis docs to Gemini to brainstorm feature ideas.
What We Heard From RedMonk Analysts—And Why Agentic Access Needs a New Security Model
Model Context Protocol (MCP) is here, and LLMs are already making requests to your internal systems. The existing security model wasn’t built for this new world of autonomous agents.
Agentic Access Management for Model Context Protocol (MCP) Workflows
We’re no longer designing systems where humans are the sole decision-makers. Agentic AI changes the rules. LLMs don’t just respond to prompts anymore, they make decisions autonomously within your systems.
How Pomerium Makes Access Audit Ready and Turns It Into a Source of Truth
Ask most teams to show who accessed a sensitive system—and why—and you’ll get a long pause.
How Pomerium Secures Access for Human, Service, and Agent Identities
Legacy tools were designed for single perimeters: users in offices, apps in one environment, and static roles assigned to each.
Not All Zero Trust Is Created Equal: Why Enterprises Host Their Own
That’s the starting point for Zero Trust. It’s a model built on verifying every user, securing every request, and removing trust based on network location.
How Pomerium Brings Zero Trust to Legacy, Hybrid, and Cloud-Native Environments
Enterprise infrastructure doesn't live in just one place. It spans data centers, Kubernetes clusters, cloud workloads, and SaaS tools. Some of it's old. Some of it's modern. All of it needs to be secure.
How Pomerium Secures SSH Access with Zero Trust
SSH access is often treated as a static utility, but in modern environments, implicit trust just won’t cut it. This article explores how Pomerium brings Zero Trust principles to SSH — using short-lived certificates, OAuth authentication, continuous policy enforcement, and session recording — without agents or VPNs.
12 Crucial Mobile Device Management (MDM) Features - 2025
When choosing the right Mobile Device Management (MDM) solution for your organization, focusing on essential features is key to meeting both security and operational needs. Here’s a breakdown of the top 12 essential MDM features to help you compare and select the right tool for your business. We have also included a ready-to-use questionnaire that you can utilize to evaluate the features of your shortlisted MDM solutions.
40 Unique IAM Interview Questions and Answers | 2025 Edition
Are you a founder, manager, or part of an HR team looking to hire for a position in an identity and access management (IAM) company? A fundamental understanding of IAM is crucial for success, especially if the role is technical, such as an analyst, engineer, or tech support. In this article, we've compiled 40 Identity and Access Management interview questions—ranging from basic to advanced—along with ideal answers to help you evaluate candidates effectively. Additionally, we’ve included operational and behavioral IAM interview questions to assess the candidate's overall personality and fit for the role.
8 Best Open Source Zero Trust Software Solutions
Unlike traditional security, which often grants implicit trust to users solely because they are inside the network, the Zero Trust model grants no implicit trust, and therefore continuously verifies all activity, ensuring that only the right people with the right level of access are authorized to reach the resources within the network. There are many open-source zero-trust software that facilitate this approach by ensuring that no entity, whether inside or outside the network, is trusted by default. Here are eight notable open-source Zero Trust software solutions.
Announcing FleetDM integration for adding device context to access control
Announcing our FleetDM integration to bring mobile device management into Pomerium's zero trust access control
Heimdall Reverse Proxy: Features, Alternatives, Pros-Cons
Heimdall is a reverse proxy tool, primarily used for managing and securing web traffic to internal services, often implemented in home labs, self-hosted services, or small-scale cloud environments. Heimdall reverse proxy is typically used to route traffic based on domain or path rules to the appropriate backend service. In this article, we have included Heimdall reverse proxy’s features, pros and cons, and best alternative.
The Best OAuth2 Proxy Alternative: Pomerium
An OAuth2 proxy is a reverse proxy server that sits in front of a web application or service to protect access using OAuth2 or OpenID Connect (OIDC) authentication protocols. It acts as an intermediary between the users and the backend services, ensuring that only authenticated users can access protected resources.
10 Best Open Source Mobile Device Management (MDM) Solutions
Managing mobile devices efficiently is crucial for organizations of all sizes. Mobile Device Management (MDM) is a system that enables organizations to securely manage, monitor, and control devices within their network. Despite the term "mobile" in its name, MDM isn’t limited to just cell phones—it covers a wide range of devices including smartphones, tablets, laptops, and even IoT devices. Choosing the right MDM solution involves considering various factors, so to help with this decision, we’ve shortlisted the 10 best open-source mobile device management solutions.
Context-Aware Authentication: Meaning, Tools, Examples
In this article, we'll explore what context-aware authentication means, share real-life examples, discuss the top implementation tools, and dive into use cases.
IAP Definition in Cybersecurity | Meaning and Solutions
In this article, we will explore IAP’s definition and meaning in both professional and layman's terms, its difference from traditional VPNs, and the top open-source platforms to enforce IAP.
The Real Lessons from the Snowflake Breach
Snowflake's breach showed companies have the Perimeter Problem, lack context-aware access control, and give third-parties too much access.
Network-centric vs Application-centric Approach
The traditional network model results in the Perimeter Problem. Here's why companies should be using the application-centric approach for better usability and security.
