authors
Eunjee Choi
Eunjee Choi articles and resources from Pomerium.
Topic archive
More from Eunjee Choi
September 2025 MCP Round‑Up: Growing Adoption Meets Rising Security Fears
September was a month of contrasts for the Model Context Protocol (MCP). On the one hand, the ecosystem matured rapidly. On the other hand, a wave of reports underscored how quickly attackers are targeting these interfaces. Researchers warned of prompt‑injection attacks, backdoored packages and a raft of newly ranked vulnerabilities, while practitioners called for stronger identity flows, fine‑grained authorization and tighter governance.
August 2025 Agentic Access and MCP Content Round‑Up: Security, Innovations & Growth
August was filled with vulnerabilities and developments in the agentic AI and Model Context Protocol (MCP) landscape. Multiple high‑severity remote‑code‑execution vulnerabilities demonstrated how easily malicious servers or modified configurations can hijack developer machines. Docker went so far as to label the MCP ecosystem a “security nightmare,” prompting calls for OAuth 2.1 authorization and zero‑trust practices. Meanwhile, vendors made notable releases and thought leaders explored the future of AI as adoption accelerates.
HIPAA & Context-Aware Access: How Pomerium Aligns with HIPAA
Healthcare organizations handle some of the most sensitive data in existence: electronic protected health information (ePHI). HIPAA’s Security Rule was designed to safeguard this data, but its requirements often feel abstract when applied to modern IT systems.
LiteLLM Alternatives: Best Open-Source and Secure LLM Gateways in 2025
As AI tools continue to evolve, more teams are deploying multiple LLMs across providers like OpenAI, Anthropic, Mistral, and Cohere. LiteLLM has become a popular gateway for abstracting away these differences, offering a unified OpenAI-compatible API to interact with over 100 models. But LiteLLM may not be the perfect fit for your team.
LiteLLM vs. Pomerium: What's the Difference and Which One Do You Need?
Compare LiteLLM and Pomerium. Learn how they differ, where they complement each other, and how to secure LLM infrastructure with the right tools.
July 2025 Agentic Access and MCP Content Round‑Up: Vulnerabilities, Governance & Growth
A number of pivotal developments marked the agentic AI and Model Context Protocol (MCP) world this past July. Two critical remote‑code‑execution flaws, one in the widely used mcp‑remote tool and another in Anthropic’s MCP Inspector , highlighted the growing security risks of AI‑agent tooling. Meanwhile, vendors released new MCP servers and training programs, and the open‑source project announced a formal governance model to sustain its rapid growth. The compiled July headlines below capture both the promise and the perils of the evolving MCP ecosystem.
Best LLM Gateways in 2025: Top Tools for Managing and Securing AI Models
Compare the top LLM gateways of 2025—including LiteLLM, OpenRouter, Kong, Pomerium, and more. Learn how to manage and secure access to OpenAI, Claude, Mistral, and other leading models.
Top 10 Articles in Agentic Access - MCP, Models, and Clients (June 2025)
June was a messy, revealing, and incredibly important month for anyone paying attention to how AI agents interact with real-world systems.
June 2025 MCP Content Round-Up: Incidents, Updates, Releases, and more!
It’s been a busy month in the world of Model Context Protocol (MCP). Between new open source server releases, security leaks, and insightful commentary from developers building on top of these tools, there’s a lot to keep up with—and even more to think about if you're working on or around AI agents. But, one thing is clear: MCP is here, and it needs to be secured .
5 Actionable Zero Trust Patterns from NIST SP 1800-35 (and How to Implement Them)
Implementing a Zero Trust Architecture (ZTA) is no longer a task that can be pushed to tomorrow—it's best practice to begin implementing it today. Understanding that moving from theory to practical implementation can be challenging, the National Institute of Standards and Technology (NIST) published Special Publication 1800-35 to provide real-world, actionable patterns to guide organizations through their Zero Trust journeys.
5 Key Takeaways about ZTA from NIST SP 1800-35
Adopting Zero Trust principles significantly reduces cybersecurity risks by ensuring only the right people, under the right circumstances, gain access to your resources.
May 2025 Data Breaches: 184M Passwords, 364K SSNs Leaked
Cyber attacks showed no signs of slowing down this past May 2025, with high-profile breaches and settlements making headlines. While the root causes behind many of these breaches remain undisclosed, a familiar pattern persists: insufficient access controls, third-party exposures, and delayed detection. These recurring weaknesses highlight the continued urgency for organizations to adopt zero-trust security principles—designed to prevent lateral movement, minimize damage, and detect anomalies before it’s too late.
Pomerium Has SOC2, and So Could You!
SOC2 is one of the most pervasive security audits in tech and sets a benchmark that a company is legit and not just a herd of cats on laptops (or at least the cat’s acceptable behavior is documented in policies and noted in risk assessments).
April 2025 Data Breaches: 4 Million SSNs Leaked, 23M+ in Settlements
Cyber attacks didn’t slow down this past April 2025, recording sizable breaches and settlements—one data breach compromised the personal identifiable data of 4 million individuals. The cause behind many of these breaches was undisclosed, however, there is a recurring theme of insufficient access controls, third-party vulnerabilities, and delayed breach detection—all weaknesses that zero-trust security measures could have addressed.
March 2025 Data Breaches: 5M+ Impacted, $39.9M+ in Damages
March 2025 saw yet another wave of significant cyber incidents affecting organizations across industries, with over 5 million individuals impacted and damages exceeding $39.9 million from just three settlements alone. These breaches reinforce a crucial reality: successful attacks rarely require sophisticated tactics, but instead exploit widespread gaps in basic security measures.
VPNs Are Increasing Your Attack Surface—Here’s Why That’s a Problem
For decades, VPNs have been the go-to solution for remote access, giving employees, contractors, and partners a way to securely connect to internal systems. The logic seemed sound: create an encrypted tunnel, protect corporate resources from the open internet, and allow only authorized users inside.
Key Insights and Lessons from the KELA 2024 Report
Cybercrime is evolving rapidly, and the KELA 2024 State of Cybercrime Report sheds light on the latest trends, attack tactics, and defensive strategies . If you don’t have time to read the full report, don’t worry—we did it for you. Here’s what you need to know.
Executive Order 14144: Strengthening Cybersecurity — Key Mandates & Zero Trust
The U.S. government continues to push for stronger cybersecurity standards as demonstrated by Executive Order (EO) 14144 . Signed on January 16, 2025, this order builds on previous cybersecurity directives by enhancing Zero Trust adoption, securing identity and access management, and strengthening software supply chain security.
February 2025 Data Breaches [LIST]
The cyber threat landscape is becoming increasingly more complex thanks to advancements in technology, but many of our data breaches today can be traced back to a relatively simple cause: compromised credentials.
Context-Based Access Control and Zero Trust: Key Insights from the CSA White Paper
The Cloud Security Alliance (CSA) recently released a white paper on Context-Based Access Control (CBAC) and its role in advancing Zero Trust security models. The paper underscores the necessity of shifting from static, trust-based access control to real-time, adaptive authentication that evaluates risk dynamically, and Pomerium was highlighted as a key player in the CBAC space.
What You Need to Know From the 2024 ITRC Data Breach Report
What You Need to Know From the 2024 ITRC Data Breach Report
January 2025 Data Breaches [LIST]
According to the 2024 Annual Data Breach Report by the Identity Theft Resource Center, there were more than 1.7 million victim notices, “a measure of the scale of events and impacts on individuals,” last year, a number that was triple that of 2023. With 3,158 total compromises recorded in 2024, it’s no surprise that this past January 2025 was also full of data breaches.
The New Frontier: AI Companies Require New Approaches to Security
AI companies are fundamentally different, and the industry is unlike anything we’ve seen before. While there are surface-level similarities to other high-tech organizations in how they operate (e.g. commonalities like Kubernetes, cloud-native architectures, and a reliance on everything-as-code), the reality is far more nuanced. AI companies face evolving and unprecedented challenges and dynamics that make their security and operational needs fundamentally different from those of other industries.
Common Pitfalls and 5 Must-Dos When Creating a Password
Passwords are like the locks on your digital front doors, but many of us are still putting flimsy padlocks on million-dollar safes. Attackers know this, and they exploit predictable patterns, laziness, and outdated ideas of what “secure” really means to breach our data.
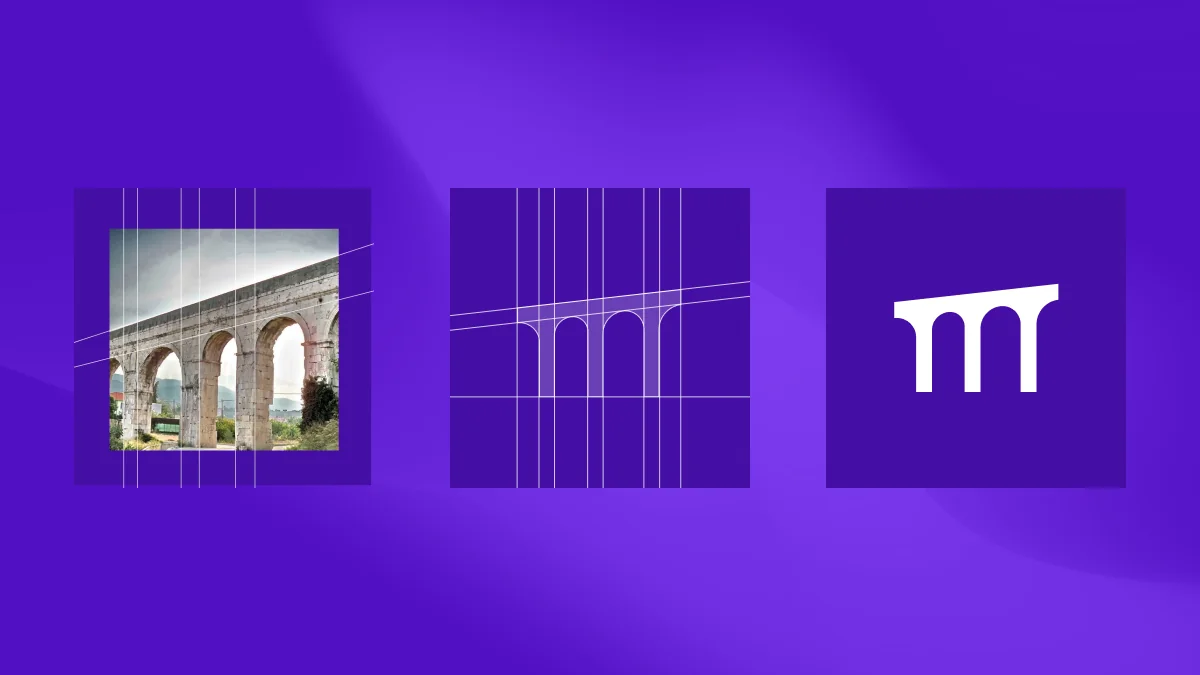
What is a "Pomerium"?
When I first started developing the idea for Pomerium, choosing the name wasn’t just an afterthought—it was a deliberate decision to align the company’s mission with a concept that’s both historically significant and deeply relevant to the challenges of modern cybersecurity.
December 2024 Data Breaches [LIST]
December 2024's biggest security breaches and data breach headlines in entertainment, finance, healthcare, infrastructure, tech, and retail.
November 2024 Data Breaches [LIST]
November 2024's biggest security breaches and data breach headlines in entertainment, finance, healthcare, infrastructure, retail, tech, healthcare, and more.
October 2024 Data Breaches [LIST]
October 2024's biggest security breaches and data breach headlines in entertainment, finance, healthcare, infrastructure, retail, tech, healthcare, and more.
September 2024 Data Breaches [LIST]
Data breach headlines from September 2024 in finance, healthcare, retail, tech, healthcare, and more.
