categories
Large Language Models (LLMs)
Browse Pomerium articles in the Large Language Models (LLMs) category.
Topic archive
Resources Categorized: Large Language Models (LLMs)
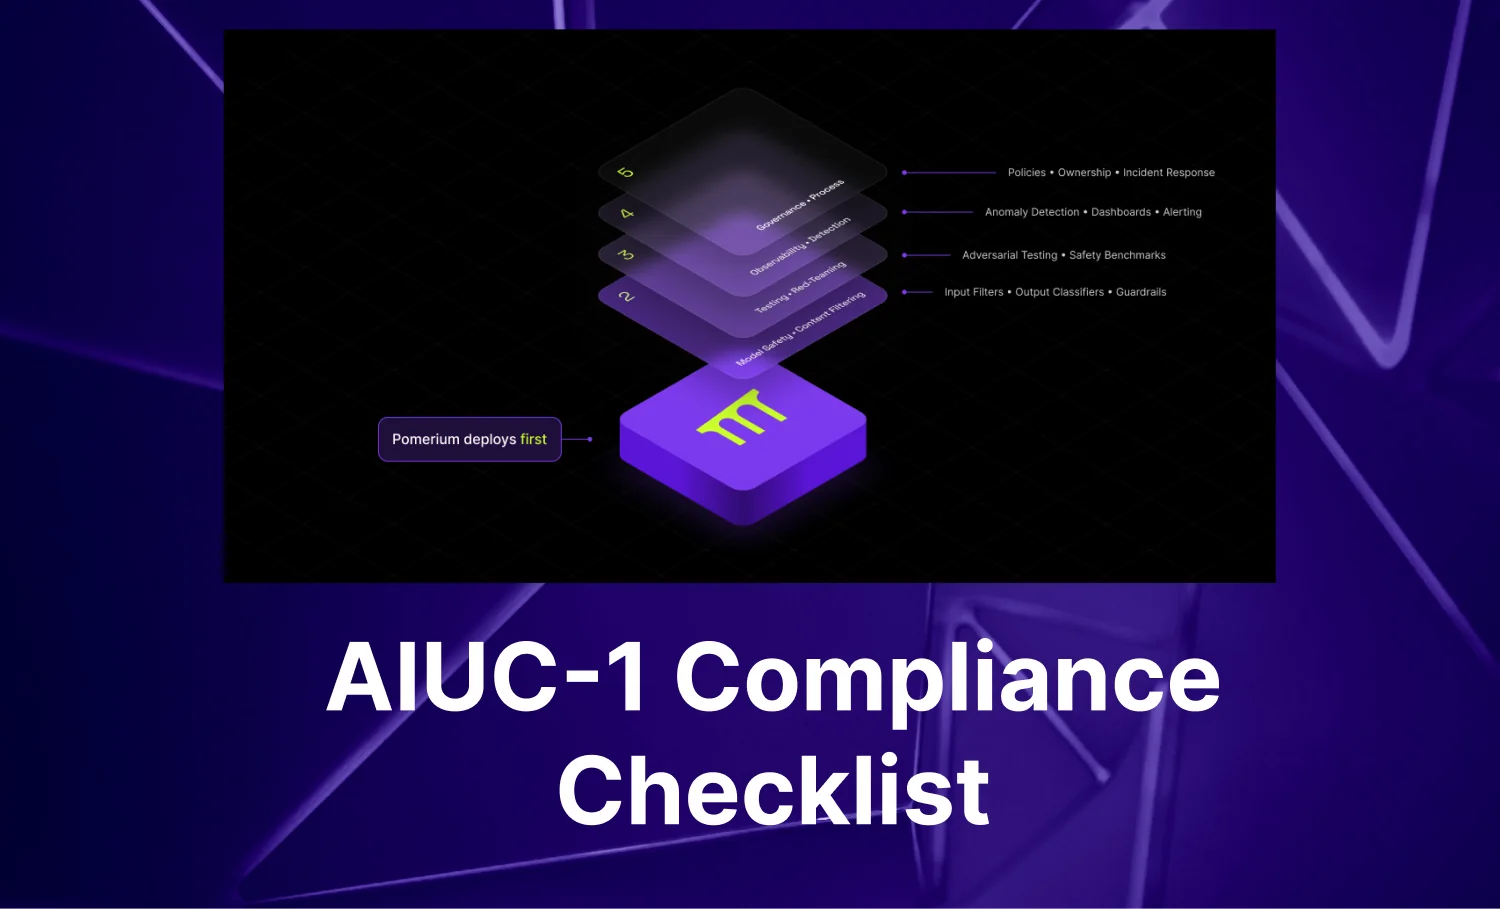
The AIUC-1 Compliance Checklist: 5 Layers Every Enterprise Needs Before Deploying AI Agents
A quick-reference checklist for AIUC-1 compliance. Five layers, 28 controls, one page. Print it, pin it, pass the audit.
The OWASP Top 10 for LLMs and How to Defend Against Them
TL;DR — The OWASP Top 10 for Large Language Model (LLM) applications highlights prompt injection, insecure output handling, and data exposure as critical risks. This guide walks through the Top 10 and shows where Zero Trust access controls, starting free with Pomerium Zero , are most effective: LLM01 Prompt Injection and LLM02 Sensitive Information Disclosure.
LiteLLM Alternatives: Best Open-Source and Secure LLM Gateways in 2025
As AI tools continue to evolve, more teams are deploying multiple LLMs across providers like OpenAI, Anthropic, Mistral, and Cohere. LiteLLM has become a popular gateway for abstracting away these differences, offering a unified OpenAI-compatible API to interact with over 100 models. But LiteLLM may not be the perfect fit for your team.
LiteLLM vs. Pomerium: What's the Difference and Which One Do You Need?
Compare LiteLLM and Pomerium. Learn how they differ, where they complement each other, and how to secure LLM infrastructure with the right tools.
Why the Managed Context Protocol (MCP) Spec Still Leaves Gaping Security Holes
TL;DR — MCP gives AI agents a shared way to invoke tools and complete tasks. But the spec lacks core security features. There is no built-in authorization, no identity enforcement, and no way to apply context-aware policy. Teams relying on reference servers are exposing internal APIs without guardrails. Pomerium applies Zero Trust controls to every request, adding identity, context, and policy enforcement at Layer 7.
Best LLM Gateways in 2025: Top Tools for Managing and Securing AI Models
Compare the top LLM gateways of 2025—including LiteLLM, OpenRouter, Kong, Pomerium, and more. Learn how to manage and secure access to OpenAI, Claude, Mistral, and other leading models.
Your Employees Are Already Dumping Company Data to LLMs (Here’s What To Do About It)
It's happening right now, in your organization. That senior developer just pasted your global auth tokens into ChatGPT to debug a tricky race condition. Your data analyst uploaded last quarter's customer churn data to Claude to help write their board presentation. Your product manager is feeding competitive analysis docs to Gemini to brainstorm feature ideas.
Best Model Context Protocol (MCP) Servers in 2025
The Model Context Protocol (MCP) is an open standard that connects Large Language Models (LLMs) to real-world tools and data. While static chatbots like ChatGPT and Claude can summarize and respond, autonomous agents need more—they need structured, real-time context.
Agentic Access Management for Model Context Protocol (MCP) Workflows
We’re no longer designing systems where humans are the sole decision-makers. Agentic AI changes the rules. LLMs don’t just respond to prompts anymore, they make decisions autonomously within your systems.
