tags
CyberSecurity
Browse Pomerium articles tagged CyberSecurity.
Topic archive
Resources Tagged: CyberSecurity
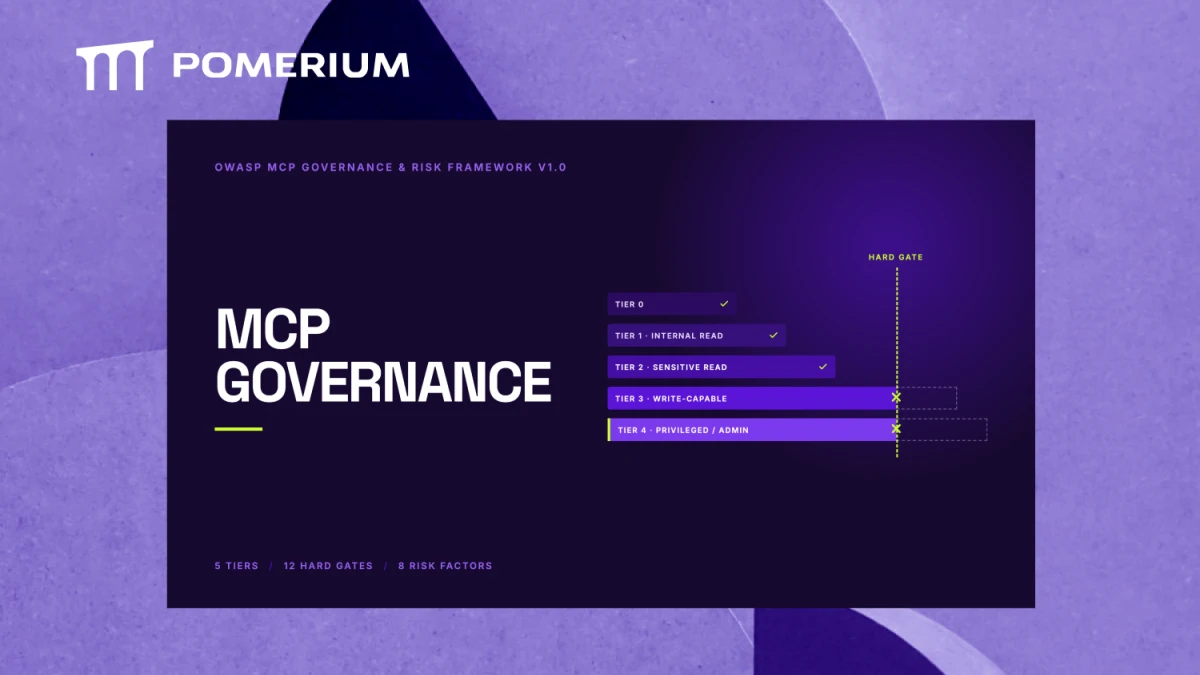
MCP Governance: What the OWASP Framework Requires, and Where Enforcement Has to Live
The OWASP MCP Governance & Risk Framework v1.0 sets tiers, hard gates, and audit rules for AI agents. Here's what it requires and how to enforce it at runtime.
Your IAM Was Built for People. Your Biggest Identity Problem Isn't People Anymore.
Every enterprise identity program was designed around a simple assumption: the thing logging in is a person. A person with a password, an MFA device, a predictable workday, and a manager who approves their access.
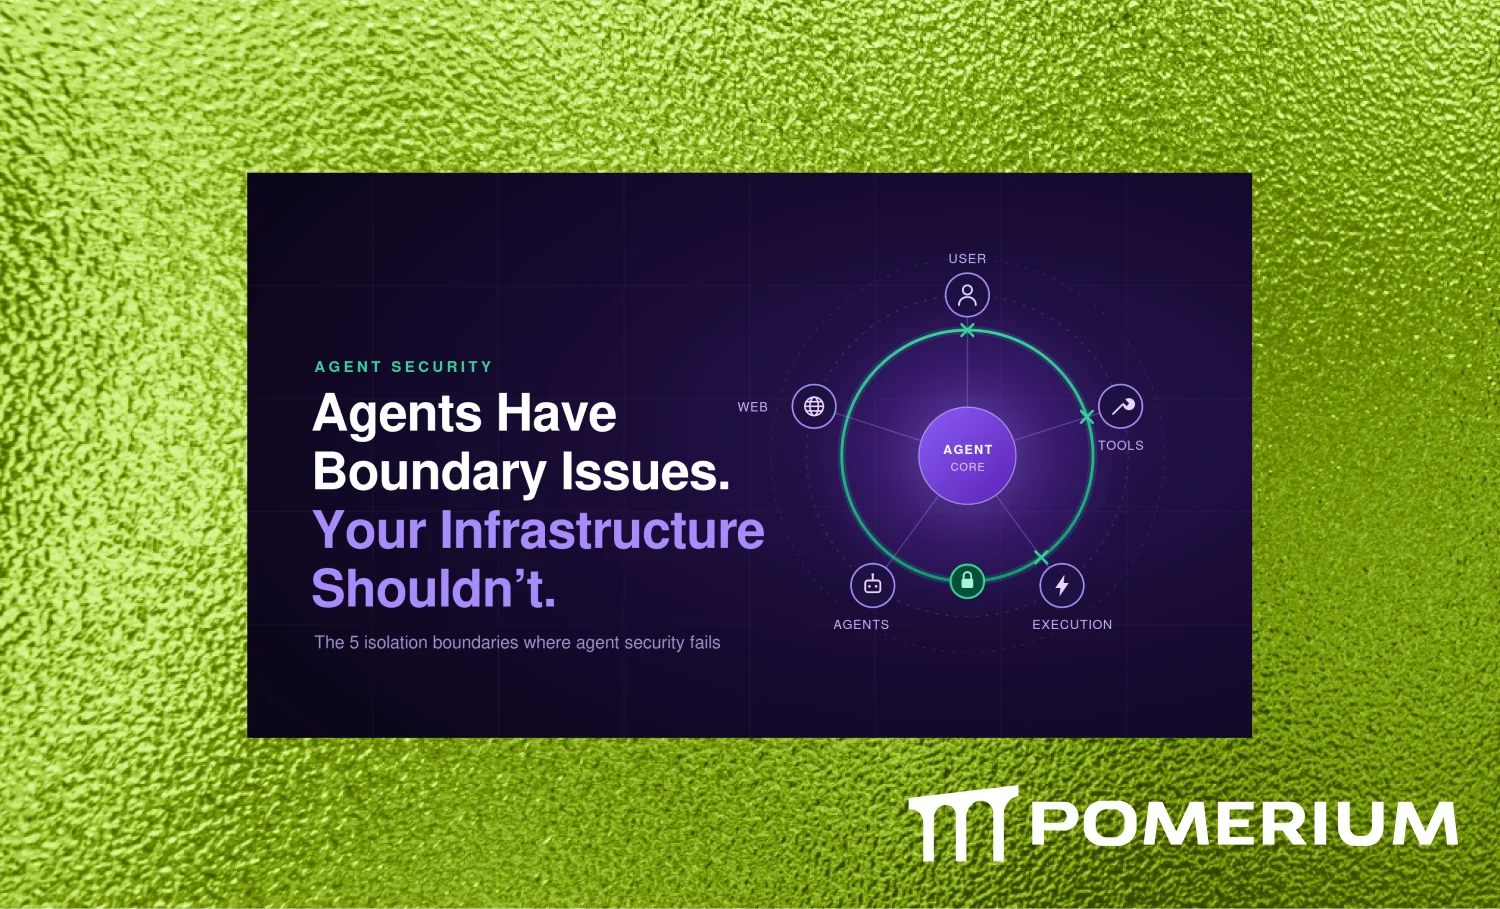
Agents Have Boundary Issues. Your Infrastructure Shouldn't.
Why the five isolation boundaries in agent security research all point to the same conclusion: enforcement has to live outside the model.
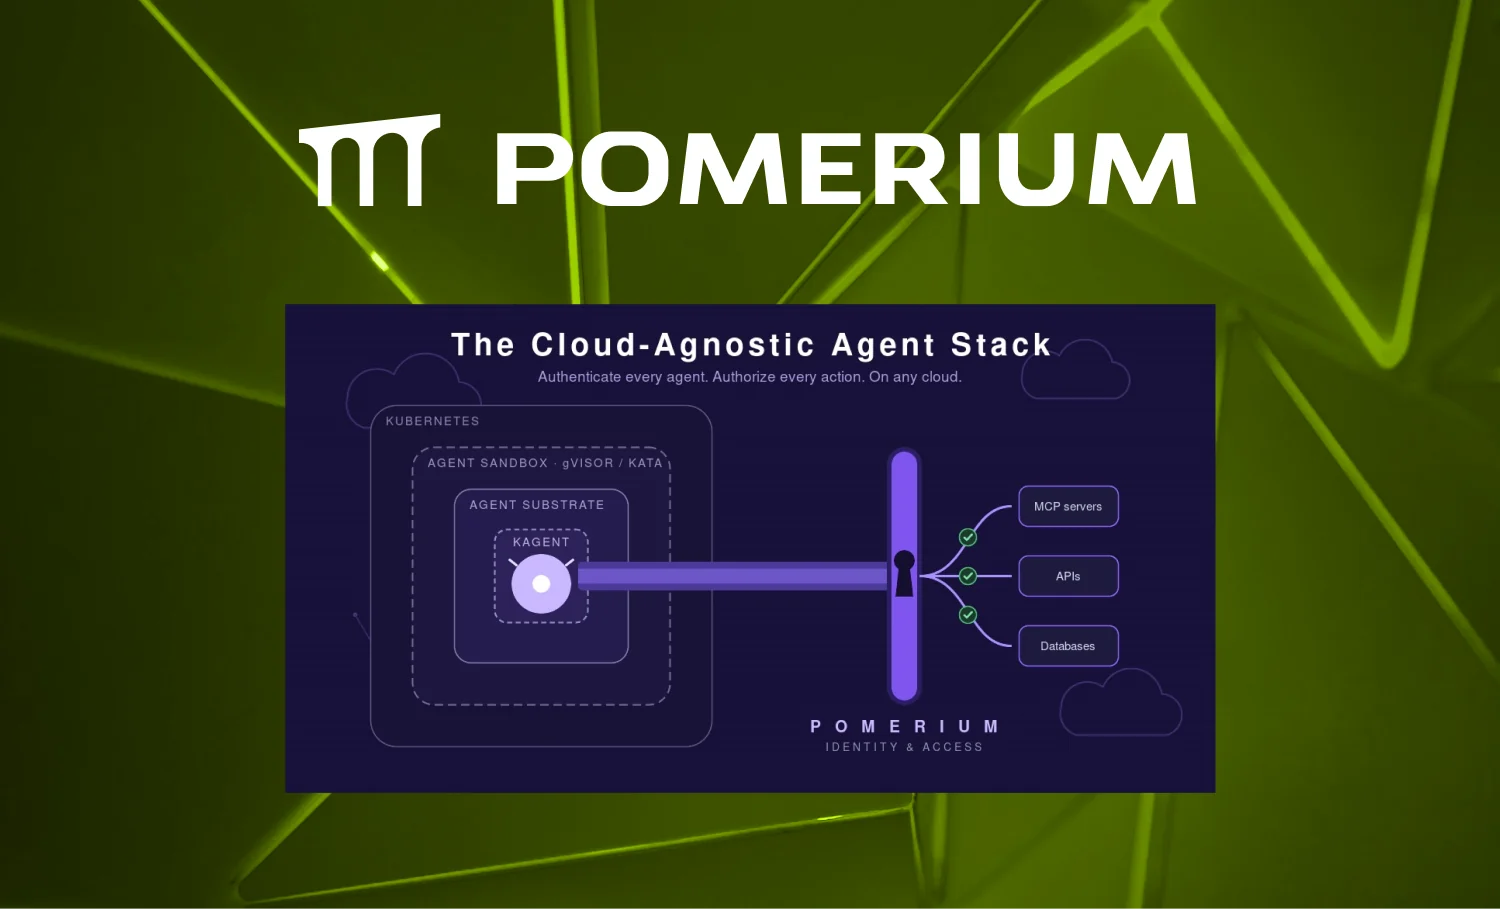
Google Built an Agent Runtime on Kubernetes. Here's How to Build a Cloud-Agnostic One with Identity Included
Google spent the last year quietly admitting what we already knew: Kubernetes was never designed to run AI agents. As Janakiram MSV writes in The New Stack , Google's GKE Agent Sandbox and the new Agent Substrate project amount to an indirect admission "that the platform that won the container decade is not the right control plane for AI agents."
How We Designed a Tamper-Evident SSH Recording System for Zero-Trust infrastructure
Pomerium is a self-hosted zero-trust access proxy that secures access to applications, services, and infrastructure. Zero trust is a security model built around the idea that no user, device, or system should be implicitly trusted. Every request must be authenticated, authorized, and evaluated before access is granted.
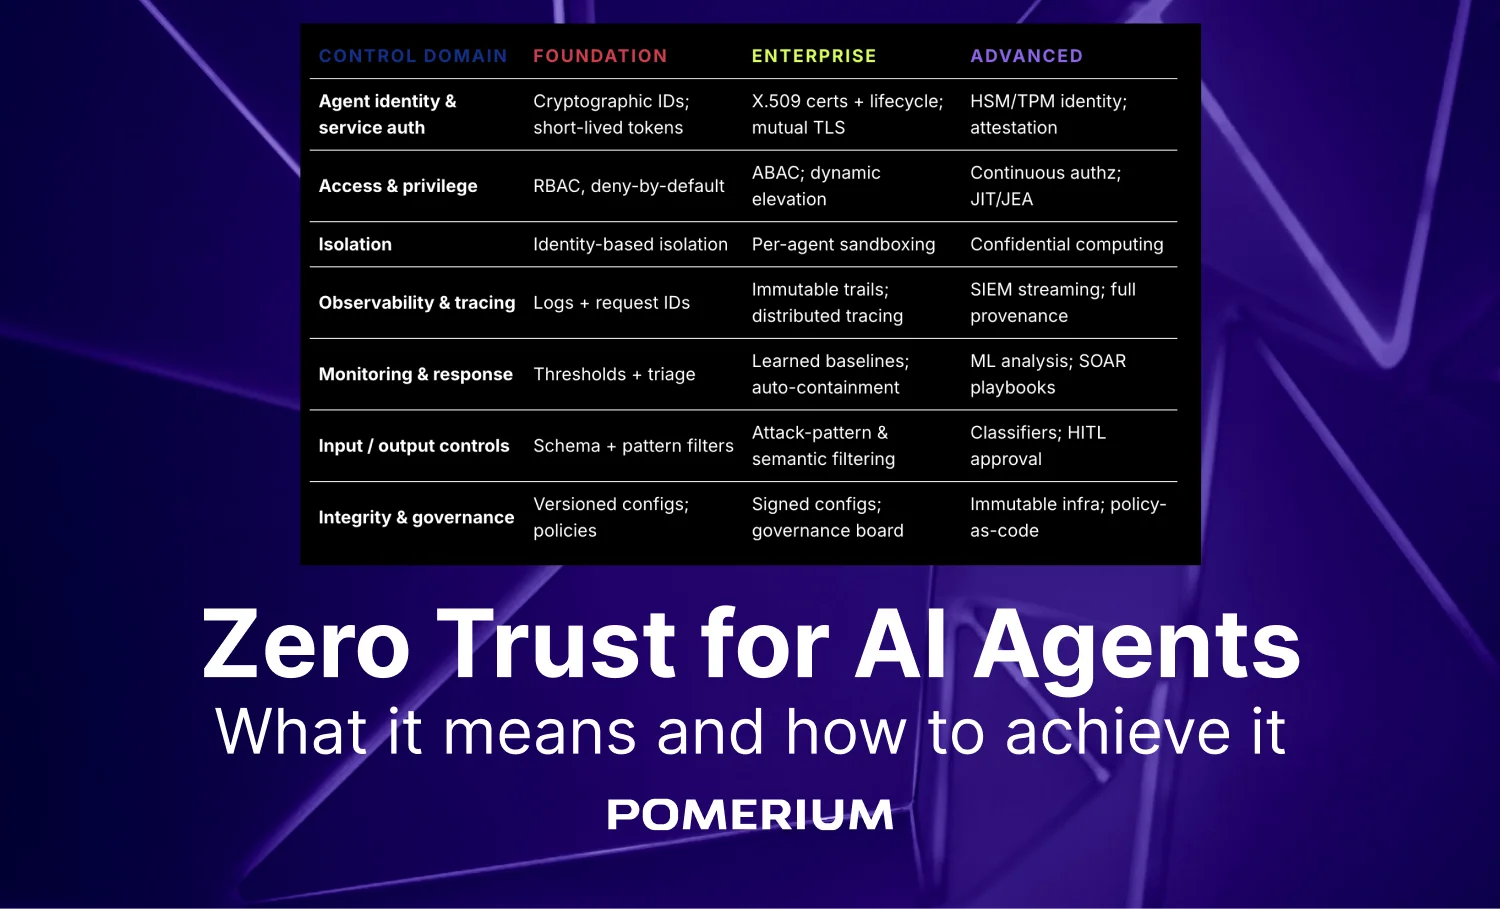
Understanding Anthropic's Zero Trust for AI Agents Guide
Most writing about AI agent security stops at the scary part: agents can be prompt-injected, they hold credentials, they act near production. True, and not very useful. However, the implementation half of Anthropic's Zero Trust for AI Agents guide is more interesting because it stops describing the problem and starts grading the solutions. It lays out exactly which controls count as table stakes, which are enterprise-grade, and which are reserved for the highest-stakes environments.
Another GlobalProtect bypass, another reminder that the VPN is the wrong place to put your trust
The Register reported today that CVE-2026-0257 , an authentication bypass in Palo Alto's GlobalProtect, has moved from a quiet medium-severity advisory to confirmed exploitation in the wild. Rapid7 traced successful attacks back to at least May 17 and reproduced the technique themselves. The flaw now sits in CISA's Known Exploited Vulnerabilities catalog with a same-day patch deadline for federal agencies.
When the Web Becomes the Attacker: AI Agent Traps and the Case for Identity-Aware Access
As autonomous AI agents fan out across the open web to read pages, call tools, and drive workflows on our behalf, the web itself becomes the attack surface. The adversary no longer needs to compromise the model, the endpoint, or the user. They only need to shape the information the agent sees. The DeepMind team calls this new class of adversarial content AI Agent Traps , and their paper is the first systematic taxonomy of them.
Top 5 Agentic Gateways for Securing MCP Tool Calls in 2026
The explosive growth of agentic AI has created a new security frontier. As large language models (LLMs) gain the ability to call external tools—through the Model Context Protocol (MCP)—organizations face an urgent question: How do you control what tools an agent can access, what parameters it can pass, and how do you audit its actions?
Why Identity-Aware Access is the Missing Layer in Agentic Security
A new VentureBeat analysis from this week lands on a truth that every enterprise security team already feels in their gut: most AI agents are a credential exfiltration waiting to happen. The monolithic agent pattern — where reasoning, execution, credential storage, and tool access all share the same process — creates a threat surface that conventional security tooling wasn't designed to close.
MCP Server Security Risks: What Development Teams Need to Know in 2026
MCP servers give AI agents direct access to your internal systems—databases, APIs, file systems—through a standardized protocol. That's powerful for building agentic workflows, but it also creates attack vectors that traditional security tools weren't designed to handle. Gartner predicts 25% of enterprise breaches by 2028 will trace back to AI agent abuse.
Complete Guide: Zero Trust for Air-Gapped Networks
Air-gapped networks are supposed to be impenetrable. No internet connection, no remote attacks. That's the theory at least. But isolation alone doesn't stop the threats that walk through the front door: compromised USB drives, malicious insiders, and supply chain attacks that arrive pre-installed on new hardware.
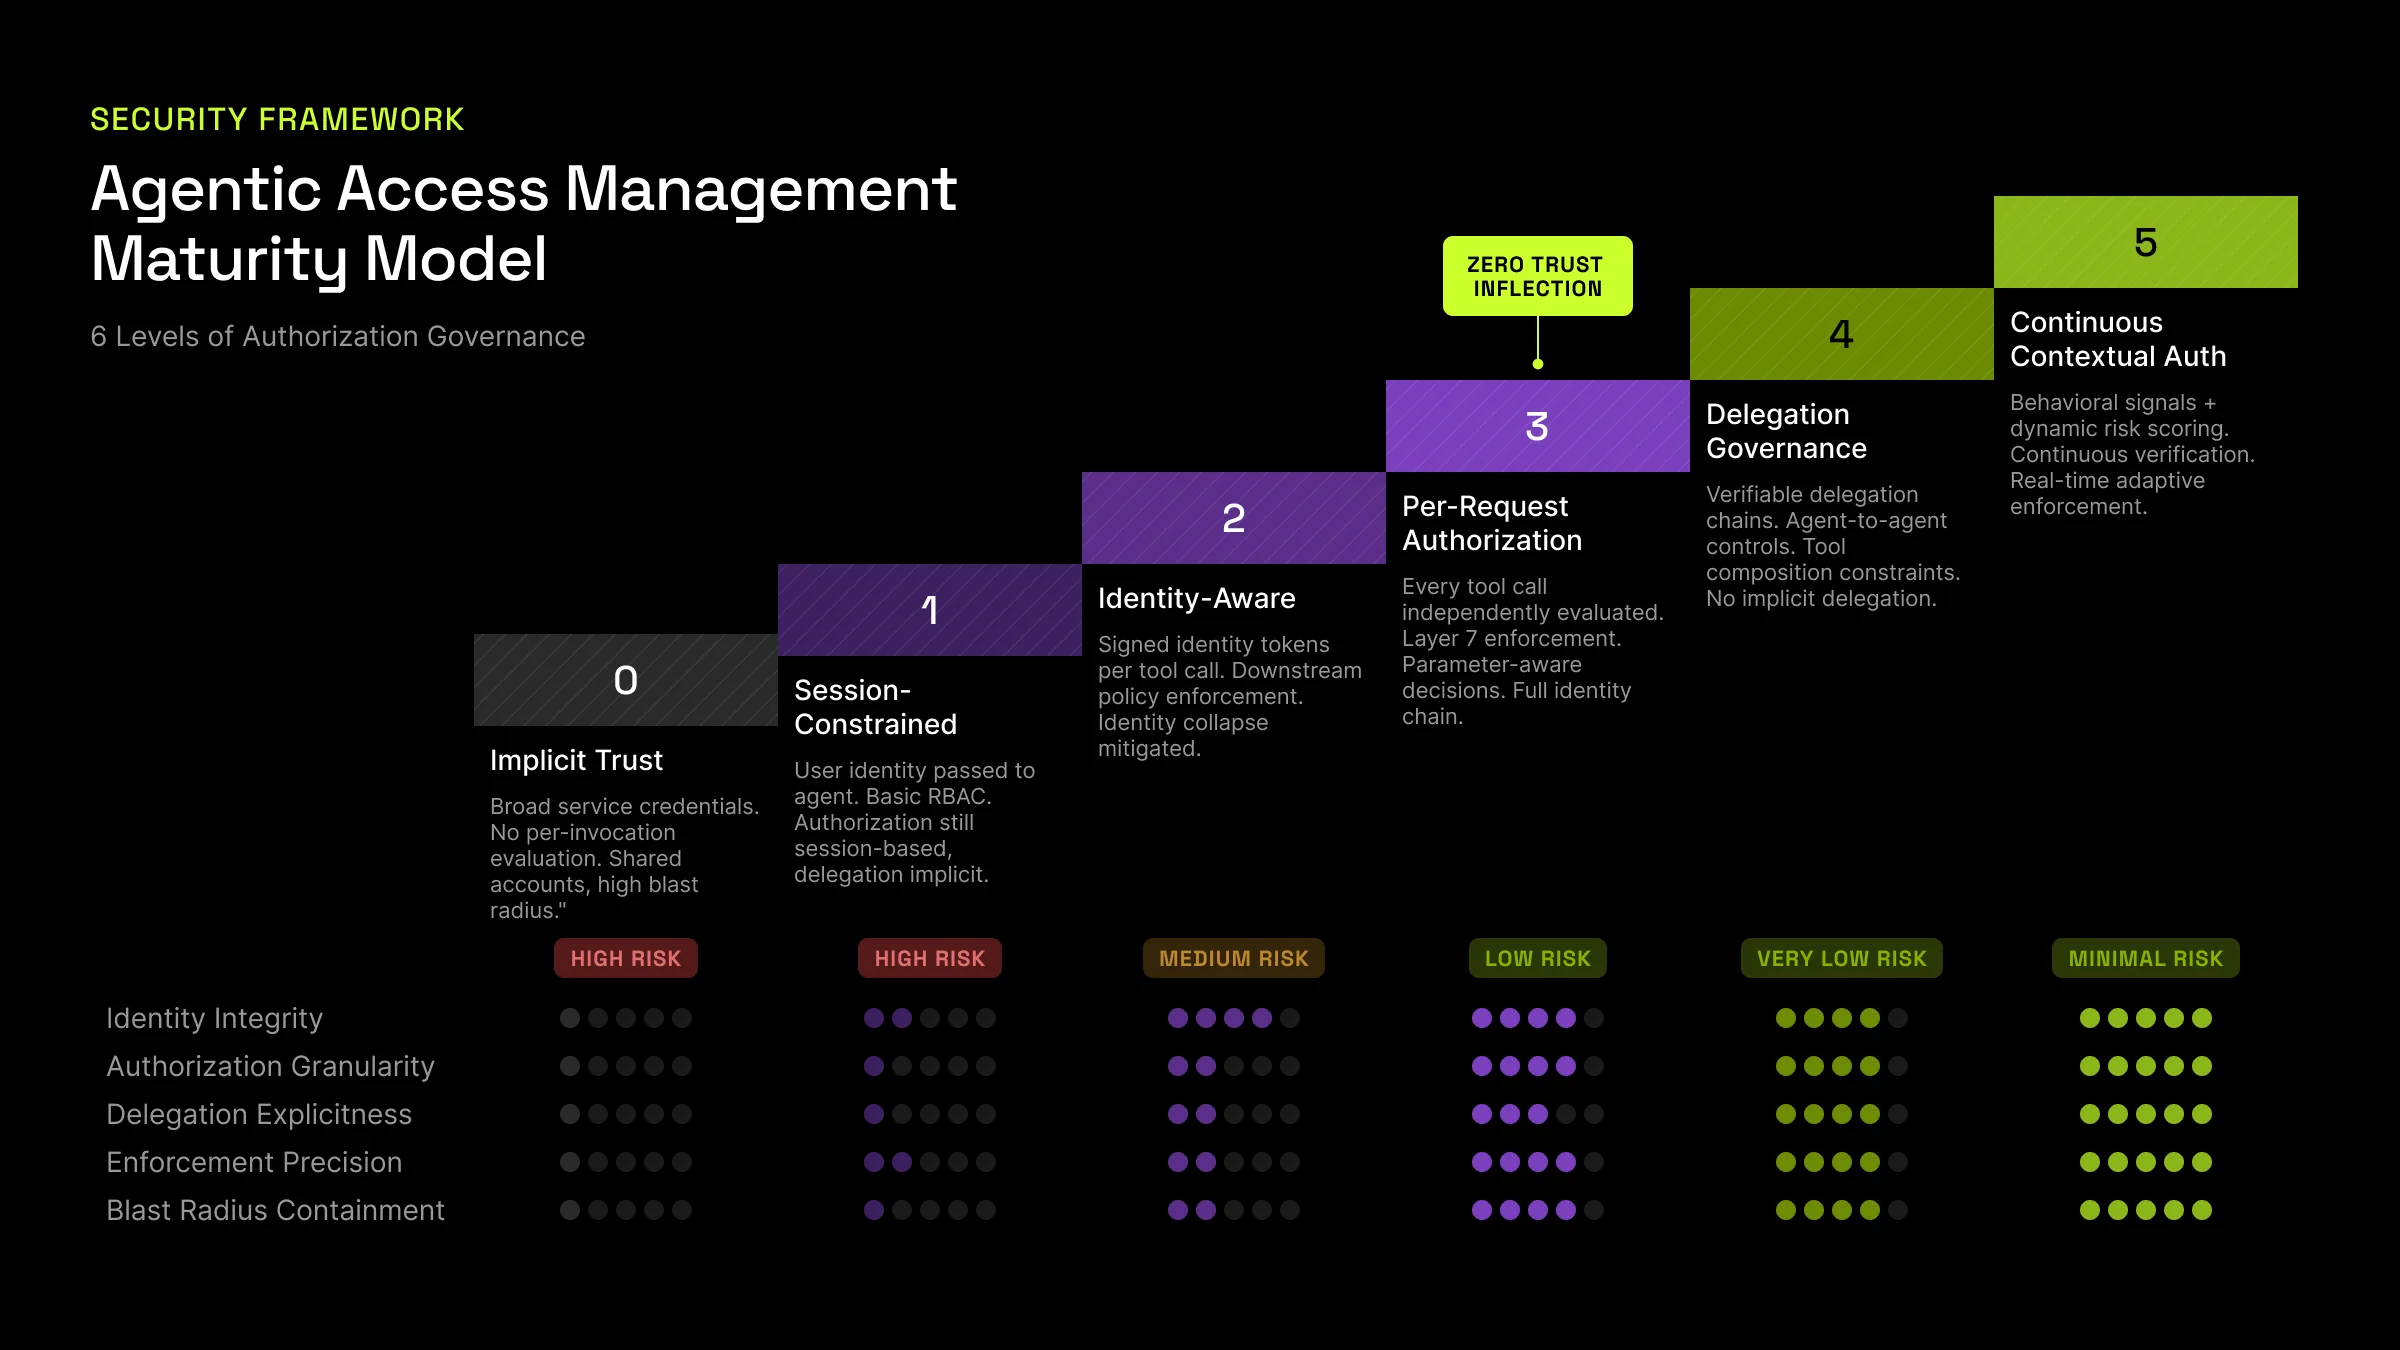
MCP Security: Why MCP Is an Authorization Crisis
A developer asks an internal AI assistant to summarize a customer support ticket and check whether a refund has already been issued. The agent retrieves the ticket, queries a billing API, updates the CRM, and returns a clean summary. Everything works exactly as designed.
7 Things to Know About Kubernetes Health Checks
At Pomerium, we help organizations run secure and resilient systems on Kubernetes. Health checks are a critical part of that work, yet they’re often difficult to configure effectively. As we expand our deployment and observability practices, we’ve been refining how we think about health checks, why they’re challenging, and the patterns that lead to reliability across different customer environments.
Turning SANS Critical AI Security Guidelines Into Enforceable Agentic Controls with Pomerium
Learn how to turn SANS Critical AI Security Guidelines into enforceable controls for access, monitoring, and governance with Pomerium.
Shadow AI Is Already in Your Org. Here’s the 5-Minute Playbook to Secure It
Shadow AI tools like ChatGPT create hidden data-leak risks. Use this zero-trust playbook to discover, govern, and secure generative AI with Pomerium.
Asana's AI Connector Leak Exposed Sensitive Data Across Organizations: What It Means for MCP Security
When news broke that Asana's MCP server had exposed sensitive data across organizations, it wasn’t just a one-off flaw. It was a warning shot for anyone integrating AI agents into their systems without guardrails.
Secure Access for Model Context Protocol (MCP)
Learn why OAuth alone can't secure the Model Context Protocol (MCP). Discover how Pomerium enforces Zero Trust for agentic AI with per-request authorization, JWT identity, and full audit logging.
How To Achieve Zero Trust In Kubernetes With Pomerium
Modern Kubernetes environments don’t have a perimeter (a single, predictable network boundary). Apps span clouds. Teams work from anywhere. Legacy security models—built on assumptions of a trusted internal network—start to fall apart.
Not All Zero Trust Is Created Equal: Why Enterprises Host Their Own
That’s the starting point for Zero Trust. It’s a model built on verifying every user, securing every request, and removing trust based on network location.
How Pomerium Brings Zero Trust to Legacy, Hybrid, and Cloud-Native Environments
Enterprise infrastructure doesn't live in just one place. It spans data centers, Kubernetes clusters, cloud workloads, and SaaS tools. Some of it's old. Some of it's modern. All of it needs to be secure.
How Pomerium Secures SSH Access with Zero Trust
SSH access is often treated as a static utility, but in modern environments, implicit trust just won’t cut it. This article explores how Pomerium brings Zero Trust principles to SSH — using short-lived certificates, OAuth authentication, continuous policy enforcement, and session recording — without agents or VPNs.
5 Reasons Chief Information and Technology Officers Are Rewriting Access Strategies for AI in 2025
Autonomous agents are here, and they’re reshaping enterprise systems. Agentic access is changing the rules — and legacy models aren’t ready for what’s coming next.
8 Docker Image Scanning Tools: 2025 and Beyond
In the previous article, we explored the top 10 Docker container scanning tools . Now, we will shift our attention to Docker image scanning tools. While many tools offer both image and container scanning capabilities, this isn't always the case—some are specialized in just one area. In this article, we’ll dive into the top Docker image scanning tools and their unique features.
7 Best Ingress Controllers for Kubernetes for 2025
Some of the best ingress controllers for Kubernetes offer robust security features: Pomerium, NGINX, Traefik, HAProxy, Envoy, Istio Ingress Gateway, and Contour.
7 Best Kubernetes Security Solutions and Vendors - 2025
Open-source Kubernetes security solutions like Pomerium, Falco, and Kubescape offer great value for teams with limited budgets. Comprehensive vendors like Aqua Security, Twistlock, and Calico Enterprise provide robust features at a higher cost.
10 Best Free Reverse Proxy Providers - Quick Guide | 2025
Here is a quick look at the 10 best free reverse proxy solutions, their use cases, supported technologies, and potential drawbacks.
20 Best Kubernetes Management Tools for 2025
Here are 20 top Kubernetes management tools to improve your K8s experience. By leveraging the right combination of tools, you can ensure your Kubernetes environments are running smoothly.
Common Pitfalls and 5 Must-Dos When Creating a Password
Passwords are like the locks on your digital front doors, but many of us are still putting flimsy padlocks on million-dollar safes. Attackers know this, and they exploit predictable patterns, laziness, and outdated ideas of what “secure” really means to breach our data.
December 2024 Data Breaches [LIST]
December 2024's biggest security breaches and data breach headlines in entertainment, finance, healthcare, infrastructure, tech, and retail.
How Pomerium Supports FedRAMP Compliance
Recently, we’ve had a lot of conversations with folks regarding whether or not Pomerium has achieved FedRAMP. We wanted to take some time to point out that while FedRAMP doesn’t apply to self-hosted software like Pomerium Core or Enterprise, there are actually specific parts of NIST SP 800-53 and FedRAMP compliance requirements that Pomerium can help you achieve.
November 2024 Data Breaches [LIST]
November 2024's biggest security breaches and data breach headlines in entertainment, finance, healthcare, infrastructure, retail, tech, healthcare, and more.
12 Zero Trust Architecture Examples With Actionable Guide
At this stage, it's safe to assume you're familiar with the core principle of Zero Trust Architecture: "never trust, always verify." Zero Trust is a framework, not a single tool you can install. So, what does a real-world zero-trust architecture example look like? What tools are necessary to achieve full zero trust implementation? In this article, we have presented a zero-trust architecture example to illustrate how a fully secured organization operates and included 12 additional zero-trust examples highlighting the features and tools required for 360-degree zero-trust protection.
What is Zscaler and How Does it Work?
If you’re evaluating a shift from traditional VPNs and considering Zscaler, this article will help. Here, we have explored what is Zscaler and how it works, its offerings, cost, pros, and cons. We have also covered how ZPA works as a VPN replacement and compared it to a promising alternative—Pomerium. Let’s begin.
Identity Aware Proxy (IAP): Meaning, Pricing, Solutions
If you’re looking to implement a zero-trust model for your organization, you’ve probably encountered the term “Identity-Aware Proxy” or “ IAP .” But what does it really mean? Which tools are best for implementing it? Is it affordable for small to medium-sized businesses, or does it come with a hefty price tag? In this article, we answer all these questions about identity-aware proxy with real-life examples. Let’s explore.
Zscaler vs. Tailscale vs. Pomerium: Detailed Comparison
If you have shortlisted Zscaler, Tailscale, and Pomerium to implement an efficient IAM solution for your distributed teams and remote infrastructure, this comparison guide will help you make a well-informed final decision. In this article, we will compare eight core features of Zscaler, Tailscale, and Pomerium to give you a comprehensive analysis of their core strengths, limitations, pricing, and ideal use cases. Let’s begin.
5 Top Tailscale Alternatives: Open Source and Paid
If you're exploring alternatives to Tailscale, this guide is here to help. Securing remote access through VPNs remains a popular method for many organizations, but not all VPNs are the same. Different types offer various features, and there are even alternatives to traditional VPNs that provide enhanced security with reduced latency.
October 2024 Data Breaches [LIST]
October 2024's biggest security breaches and data breach headlines in entertainment, finance, healthcare, infrastructure, retail, tech, healthcare, and more.
Docker Container Scanning Tools: Open Source and Paid
Selecting the right Docker container scanning tools is essential for strengthening your organization’s security posture. However, with so many options available, the decision can feel overwhelming. To simplify this process, we have handpicked 10 popular Docker container security scanners.
Kubectl Cheat Sheet with Examples- 50 Quick Commands
Whether you're a seasoned DevOps engineer or just getting started with Kubernetes, having a quick reference guide can significantly boost your productivity and confidence. In this article, we've created an ultimate Kubectl cheat sheet with 50 essential commands and examples, covering everything from basic operations to advanced configurations. This guide is designed to be your go-to resource for navigating Kubernetes efficiently, helping you execute tasks faster and with greater accuracy.
Cloudflare Access vs. Tailscale vs. Pomerium
If you have shortlisted Cloudflare Access, Tailscale, and Pomerium for your ZTNA needs but are unsure which one to choose, this article is here to guide you. These three solutions follow Zero Trust principles but vary significantly in architecture, features, and ideal use cases. This Cloudflare Access vs. Tailscale vs. Pomerium guide contains a detailed comparison of each to help you better understand their differences and make a more informed decision about your organization's security requirements.
Cloudflare Alternatives & Competitors: CDN, Zero Trust & SASE
Cloudflare offers a wide range of services, making it difficult to find a single alternative that covers all its capabilities. In this article, we've outlined Cloudflare alternatives for 1) Zero Trust and Secure Access Service Edge (SASE) , and 2) Application and Network Services, allowing you to make an informed decision based on your specific needs. So, without further delay, let’s explore!
Cyber Security Awareness Month 2024: What’s New?
Here is a list of exciting things happening across the country for Cybersecurity Awareness Month 2024! Events, conferences, and resources exclusive to this year's cyber awareness month! Check them out!
Security is Usability — Examining Cybersecurity Erosion
We examine cybersecurity erosion, the concept that security systems are only as good as their least compliant user. To avoid it, security should always be designed to be usable.
Kubernetes Compliance: NIST, CIS & PCI- Actionable Guide
Achieving Kubernetes compliance requires a careful blend of technical controls, governance policies, and security best practices. To help you in this process, we have compiled an actionable guide for Kubernetes PCI compliance, NIST container security, and CIS Kubernetes benchmark. By leveraging these best practices and tools, organizations can confidently secure their Kubernetes environments and maintain regulatory compliance.
Achieving zero trust with Pomerium JWTs
We discuss how Pomerium JWTs enable zero trust architecture for verifying each request.
September 2024 Data Breaches [LIST]
Data breach headlines from September 2024 in finance, healthcare, retail, tech, healthcare, and more.
10 Ugliest VPN Security Risks for Organizations and Users
While VPNs do provide some privacy advantages, they also come with several risks. Brace yourself, as we dive into the dark side of VPNs and unveil the top 10 VPN security risks lurking behind the mask of protection.
Zero Trust VPN: Meaning and Alternatives
Zero Trust VPN means a virtual private network service that works on the principle of "never trust, always verify." Although some VPN providers claim to offer Zero Trust VPN, in reality, most VPNs lack some core features and the users need to buy extra security products/services to implement the Zero Trust model.
Twingate Vs. Tailscale Vs. Pomerium: 6 Key Differences
Twingate is best suited for backend infrastructure security, Tailscale excels in simplifying device and network connections, and Pomerium provides robust zero-trust, application-layer security with advanced logging.
Breach Notification Letter: Samples, Templates, Examples
@seo:We've provided data breach notification letters below. 2 ready-to-use templates (general template, and GRPD breach specific), 1 Sample breach notice letter caused by exploiting third-party vendor vulnerability, 2 data breach notice letter examples
B2B VPN: Meaning, Examples, Alternatives
B2B VPN meaning: A B2B VPN (Business-to-Business Virtual Private Network) is a secure connection established between multiple business entities over the internet. Here are it's pros, cons, and alternatives
Palo Alto Clientless VPN: Pros - Cons, Alternatives
Let's explore how Palo Alto’s Clientless VPN works, its pros and cons, and whether it meets your organization's remote access needs. We'll also delve into an alternative solution that might better align with your specific requirements.
Kubernetes Reverse Proxy: Meaning and Solutions
This guide will walk you through the fundamentals of what is Kubernetes reverse proxy, how it works, its use cases, and how to set it up.
2.9 Billion Social Security Number Breach: What to Know
2024’s biggest breach compromised 2.9 billion data records, including social security numbers and other personal data from the National Public Database (NPD). Here’s what you should know.
August 2024 Newsletter
Our newsletter covers the CrowdStrike BSoD incident, the ongoing Snowflake meltdown, and an upcoming Pomerium Zero feature!
The Real Lessons from the Snowflake Breach
Snowflake's breach showed companies have the Perimeter Problem, lack context-aware access control, and give third-parties too much access.
Network-centric vs Application-centric Approach
The traditional network model results in the Perimeter Problem. Here's why companies should be using the application-centric approach for better usability and security.
CrowdStrike is a Harsh Reminder of the Danger of Third-Party Clients
The true lesson from the CrowdStrike BSOD debacle: avoid third-party clients
