categories
Authorization
Browse Pomerium articles in the Authorization category.
Topic archive
Resources Categorized: Authorization
Privilege Access Is the Past. Per Request Authorization Is the Future.
For twenty years, cybersecurity has organized itself around a single idea:
Turning SANS Critical AI Security Guidelines Into Enforceable Agentic Controls with Pomerium
Learn how to turn SANS Critical AI Security Guidelines into enforceable controls for access, monitoring, and governance with Pomerium.
What We Heard From RedMonk Analysts—And Why Agentic Access Needs a New Security Model
Model Context Protocol (MCP) is here, and LLMs are already making requests to your internal systems. The existing security model wasn’t built for this new world of autonomous agents.
Why Per-Request Authorization Is the Foundation of Zero Trust
Most access tools treat authentication like a one-time handshake. In these models, once a user or service is validated, they’re granted broad access for the rest of their session, regardless of what changes afterward.
Achieving zero trust with Pomerium JWTs
We discuss how Pomerium JWTs enable zero trust architecture for verifying each request.
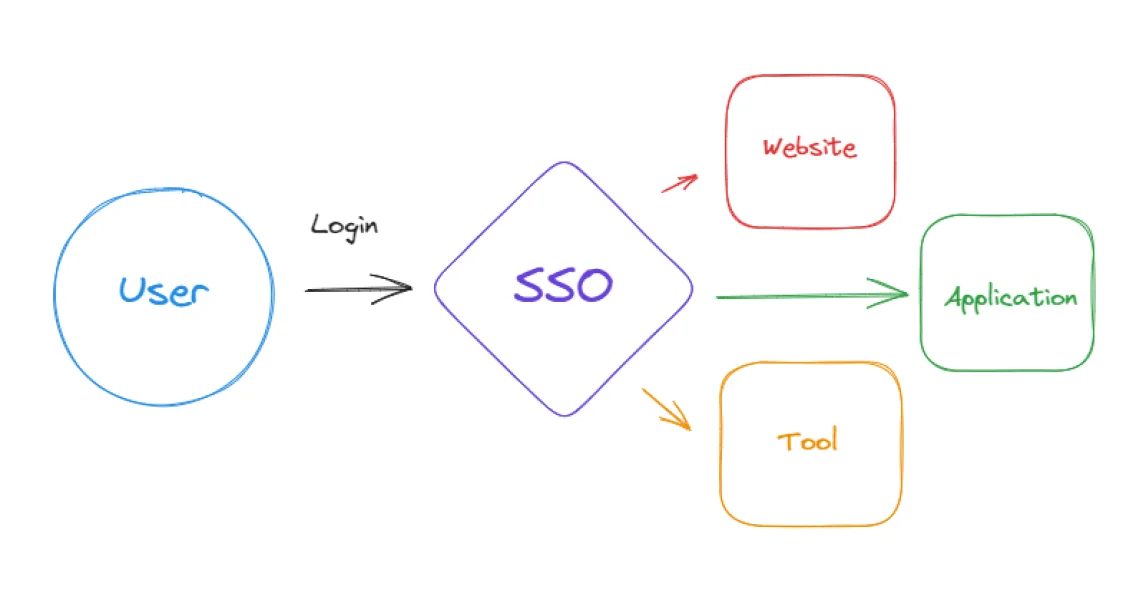
SSO: OAuth2 vs OIDC vs SAML
Single Sign-On (SSO) is a way for users to be authenticated for multiple applications and services with one process. Should you use OAuth2, OIDC, or SAML?
Authn vs. Authz — Authentication vs. Authorization
When it comes to access control, authentication (AuthN) and authorization (AuthZ) fulfill different functions as methods to control access. In the modern world, those resources can be sensitive assets, applications, programs, devices, or more.
