categories
Secure Agentic Access
Browse Pomerium articles in the Secure Agentic Access category.
Topic archive
Resources Categorized: Secure Agentic Access
IAM for Agentic AI: 6 Platforms Compared | Pomerium
Compare Pomerium, Aembit, Astrix, Token Security, Oasis, and Britive for securing AI agents and workload identities. See which platform fits your stack.
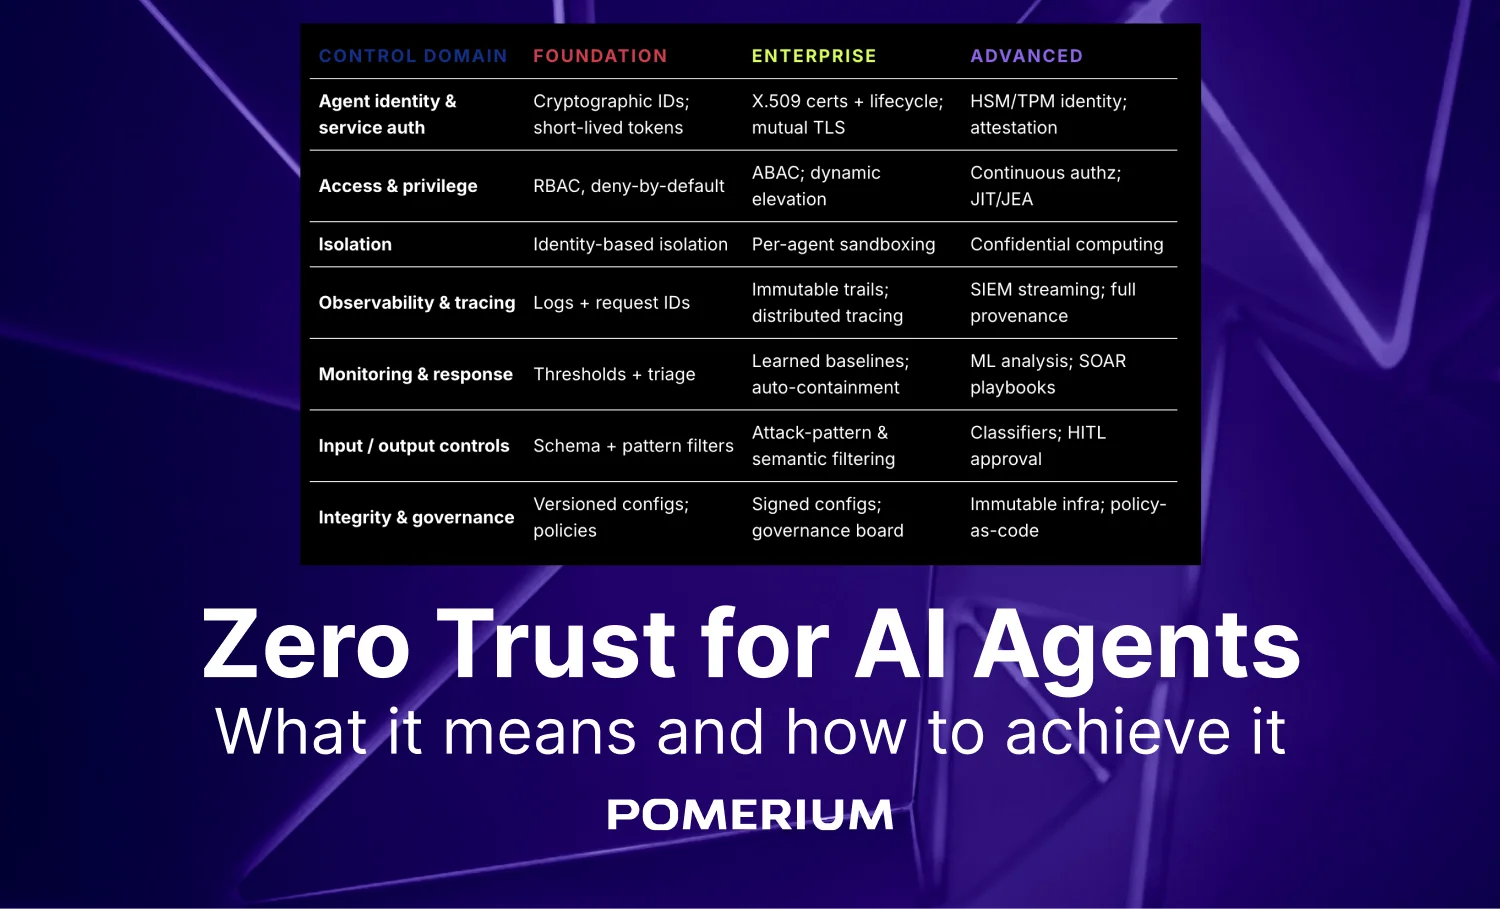
Understanding Anthropic's Zero Trust for AI Agents Guide
Most writing about AI agent security stops at the scary part: agents can be prompt-injected, they hold credentials, they act near production. True, and not very useful. However, the implementation half of Anthropic's Zero Trust for AI Agents guide is more interesting because it stops describing the problem and starts grading the solutions. It lays out exactly which controls count as table stakes, which are enterprise-grade, and which are reserved for the highest-stakes environments.
Why Identity-Aware Access is the Missing Layer in Agentic Security
A new VentureBeat analysis from this week lands on a truth that every enterprise security team already feels in their gut: most AI agents are a credential exfiltration waiting to happen. The monolithic agent pattern — where reasoning, execution, credential storage, and tool access all share the same process — creates a threat surface that conventional security tooling wasn't designed to close.
MCP Server Security Risks: What Development Teams Need to Know in 2026
MCP servers give AI agents direct access to your internal systems—databases, APIs, file systems—through a standardized protocol. That's powerful for building agentic workflows, but it also creates attack vectors that traditional security tools weren't designed to handle. Gartner predicts 25% of enterprise breaches by 2028 will trace back to AI agent abuse.
What We Heard From RedMonk Analysts—And Why Agentic Access Needs a New Security Model
Model Context Protocol (MCP) is here, and LLMs are already making requests to your internal systems. The existing security model wasn’t built for this new world of autonomous agents.
